
Reporting deadlines and stealthy intruders shape demand
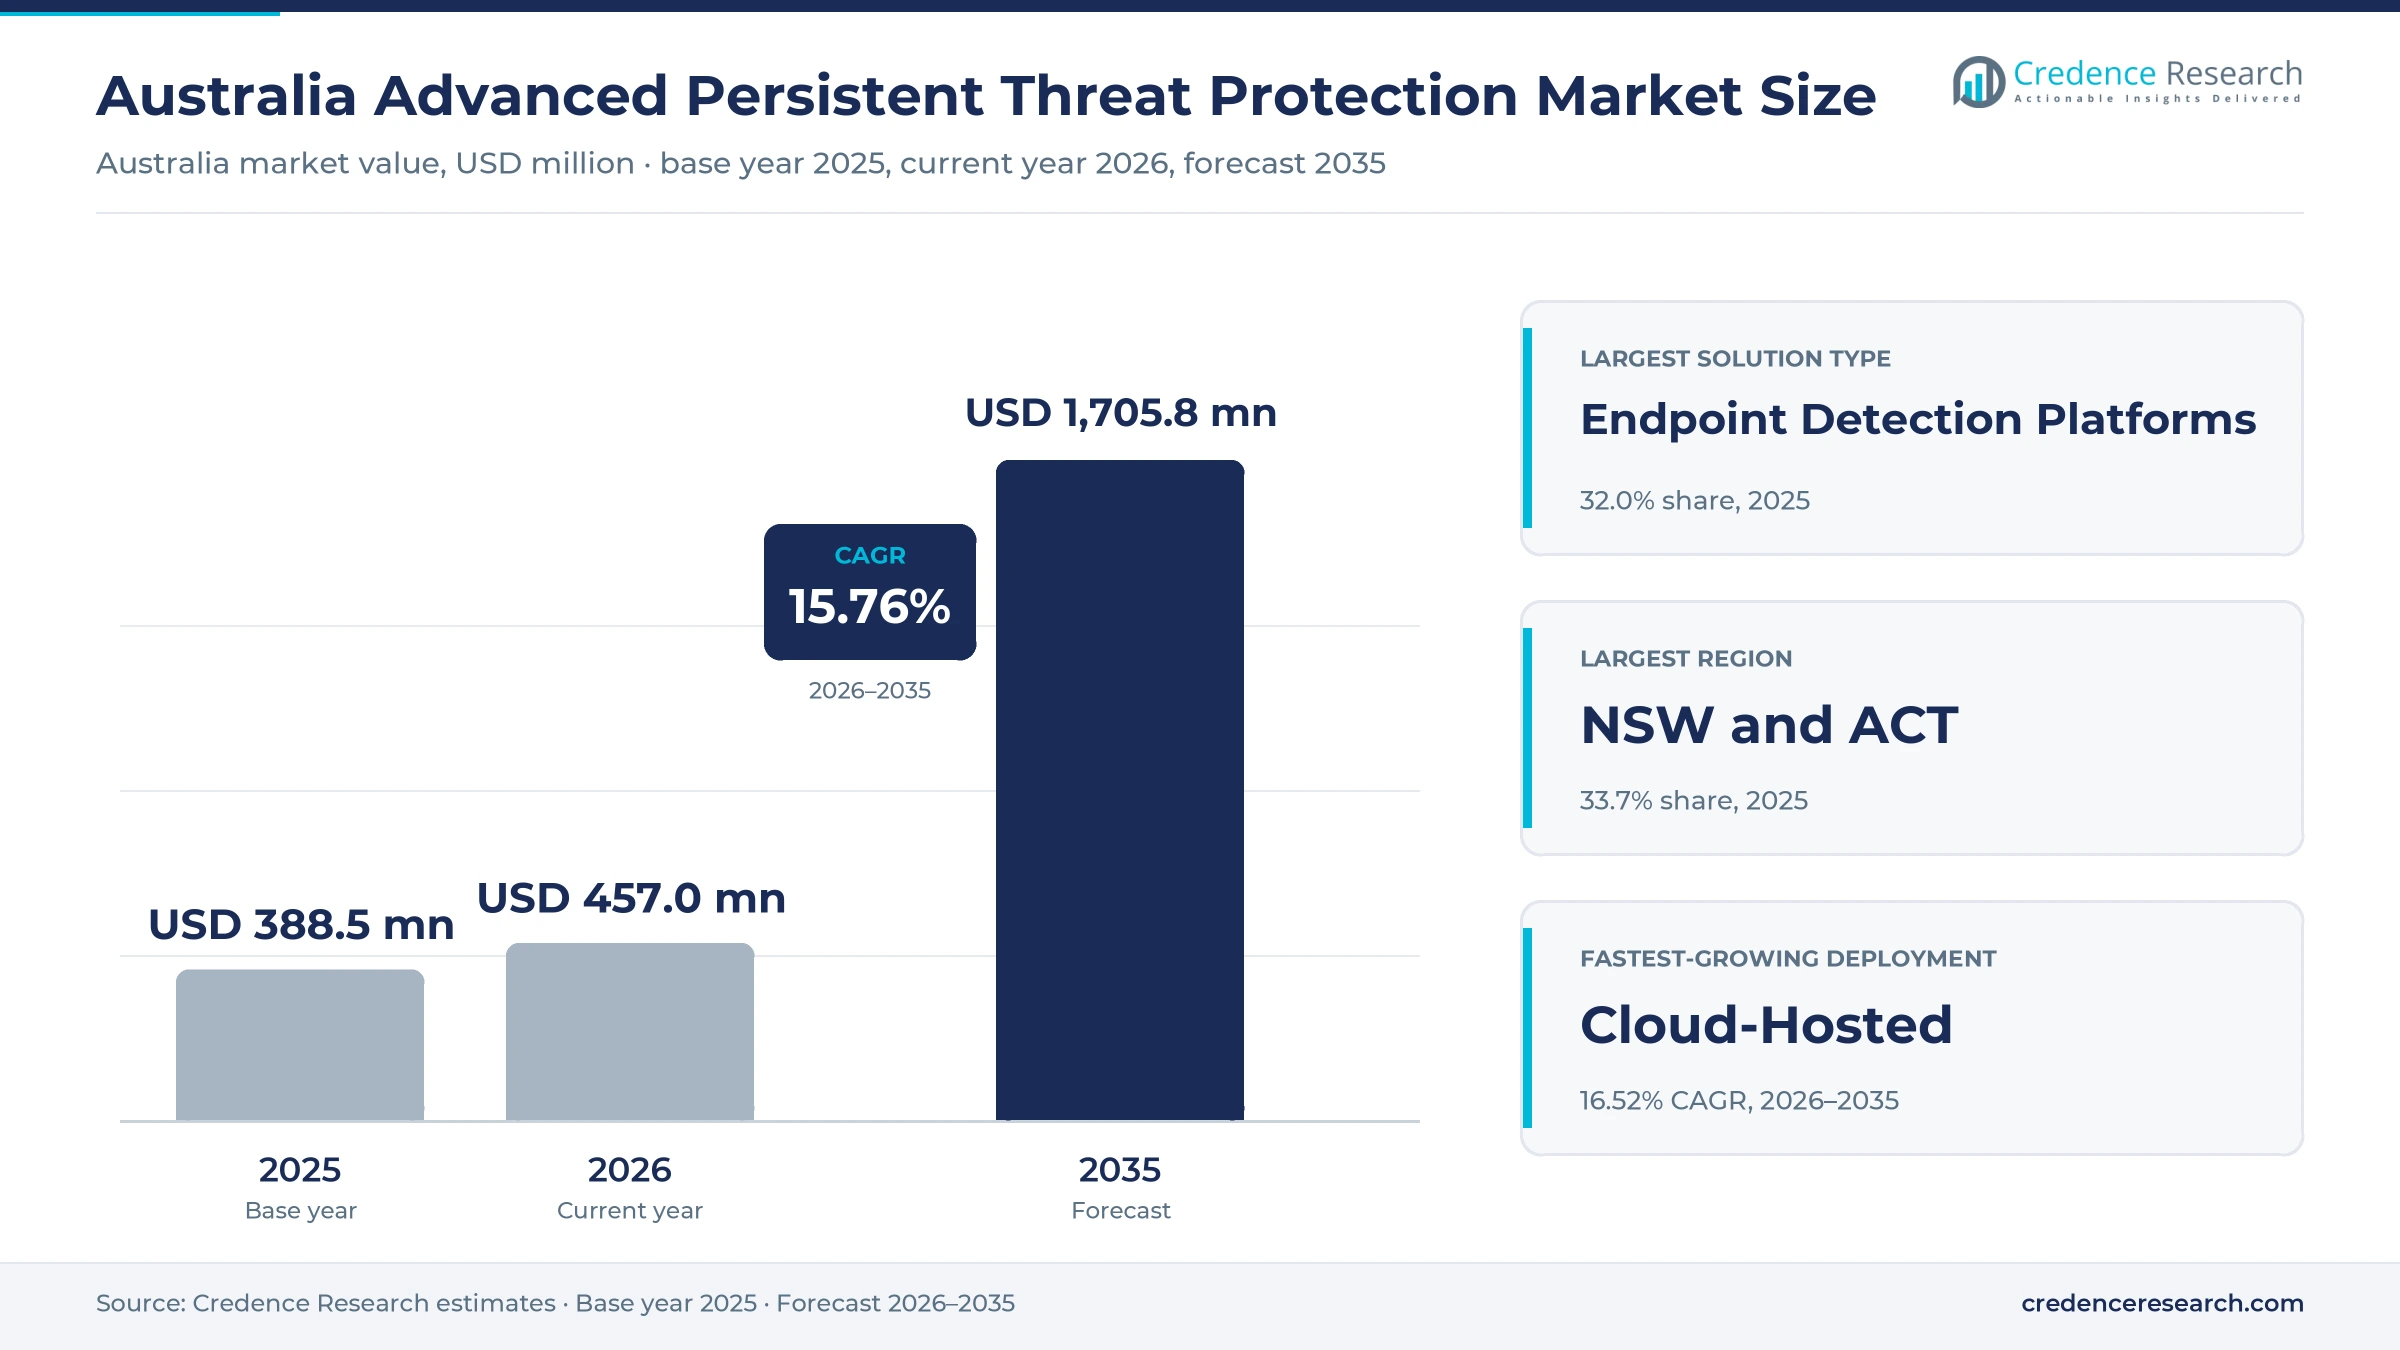
The Australia advanced persistent threat protection market was valued at USD 388.5 million in 2025 and is projected to increase from USD 457.0 million in 2026 to USD 1.71 billion by 2035, registering a CAGR of 15.76% during 2026–2035. Demand comes from banks, government agencies, infrastructure operators and large enterprises that need to find hidden intruders, contain them and prove control to regulators. New South Wales and Australian Capital Territory held the largest regional share, 33.7% in 2025, because Sydney hosts most bank and insurer head offices while Canberra concentrates federal agencies. Western Australia and South Australia is the fastest-growing region at 16.32% a year, as resources, energy and defense operators extend monitoring to operational networks. However, ransomware payment reporting under the Cyber Security Act 2024, in force since May 2025, has pushed more organizations to buy detection tools that can reconstruct an attack quickly.
Which tools and services does the national estimate cover?
The estimate measures spending by Australian organizations on tools and services built to find, block and remove long-running, targeted intrusions. It counts endpoint detection platforms, network protection platforms, security analytics platforms and specialist services such as managed detection, incident response, threat hunting and compromise assessments, bought by subscription, consumption, retainer or project.
The estimate excludes basic antivirus sold to consumers, general information technology outsourcing, identity software sold on its own and cyber insurance premiums. The value chain runs from global platform vendors and cloud providers through local integrators, security operations centers and response firms to the agencies and companies that own the protected networks.
Australia Advanced Persistent Threat Protection Market Insights
- The Australia advanced persistent threat protection market was valued at USD 388.5 million in 2025 and is projected to reach USD 1.71 billion by 2035, registering a CAGR of 15.76% during 2026–2035.
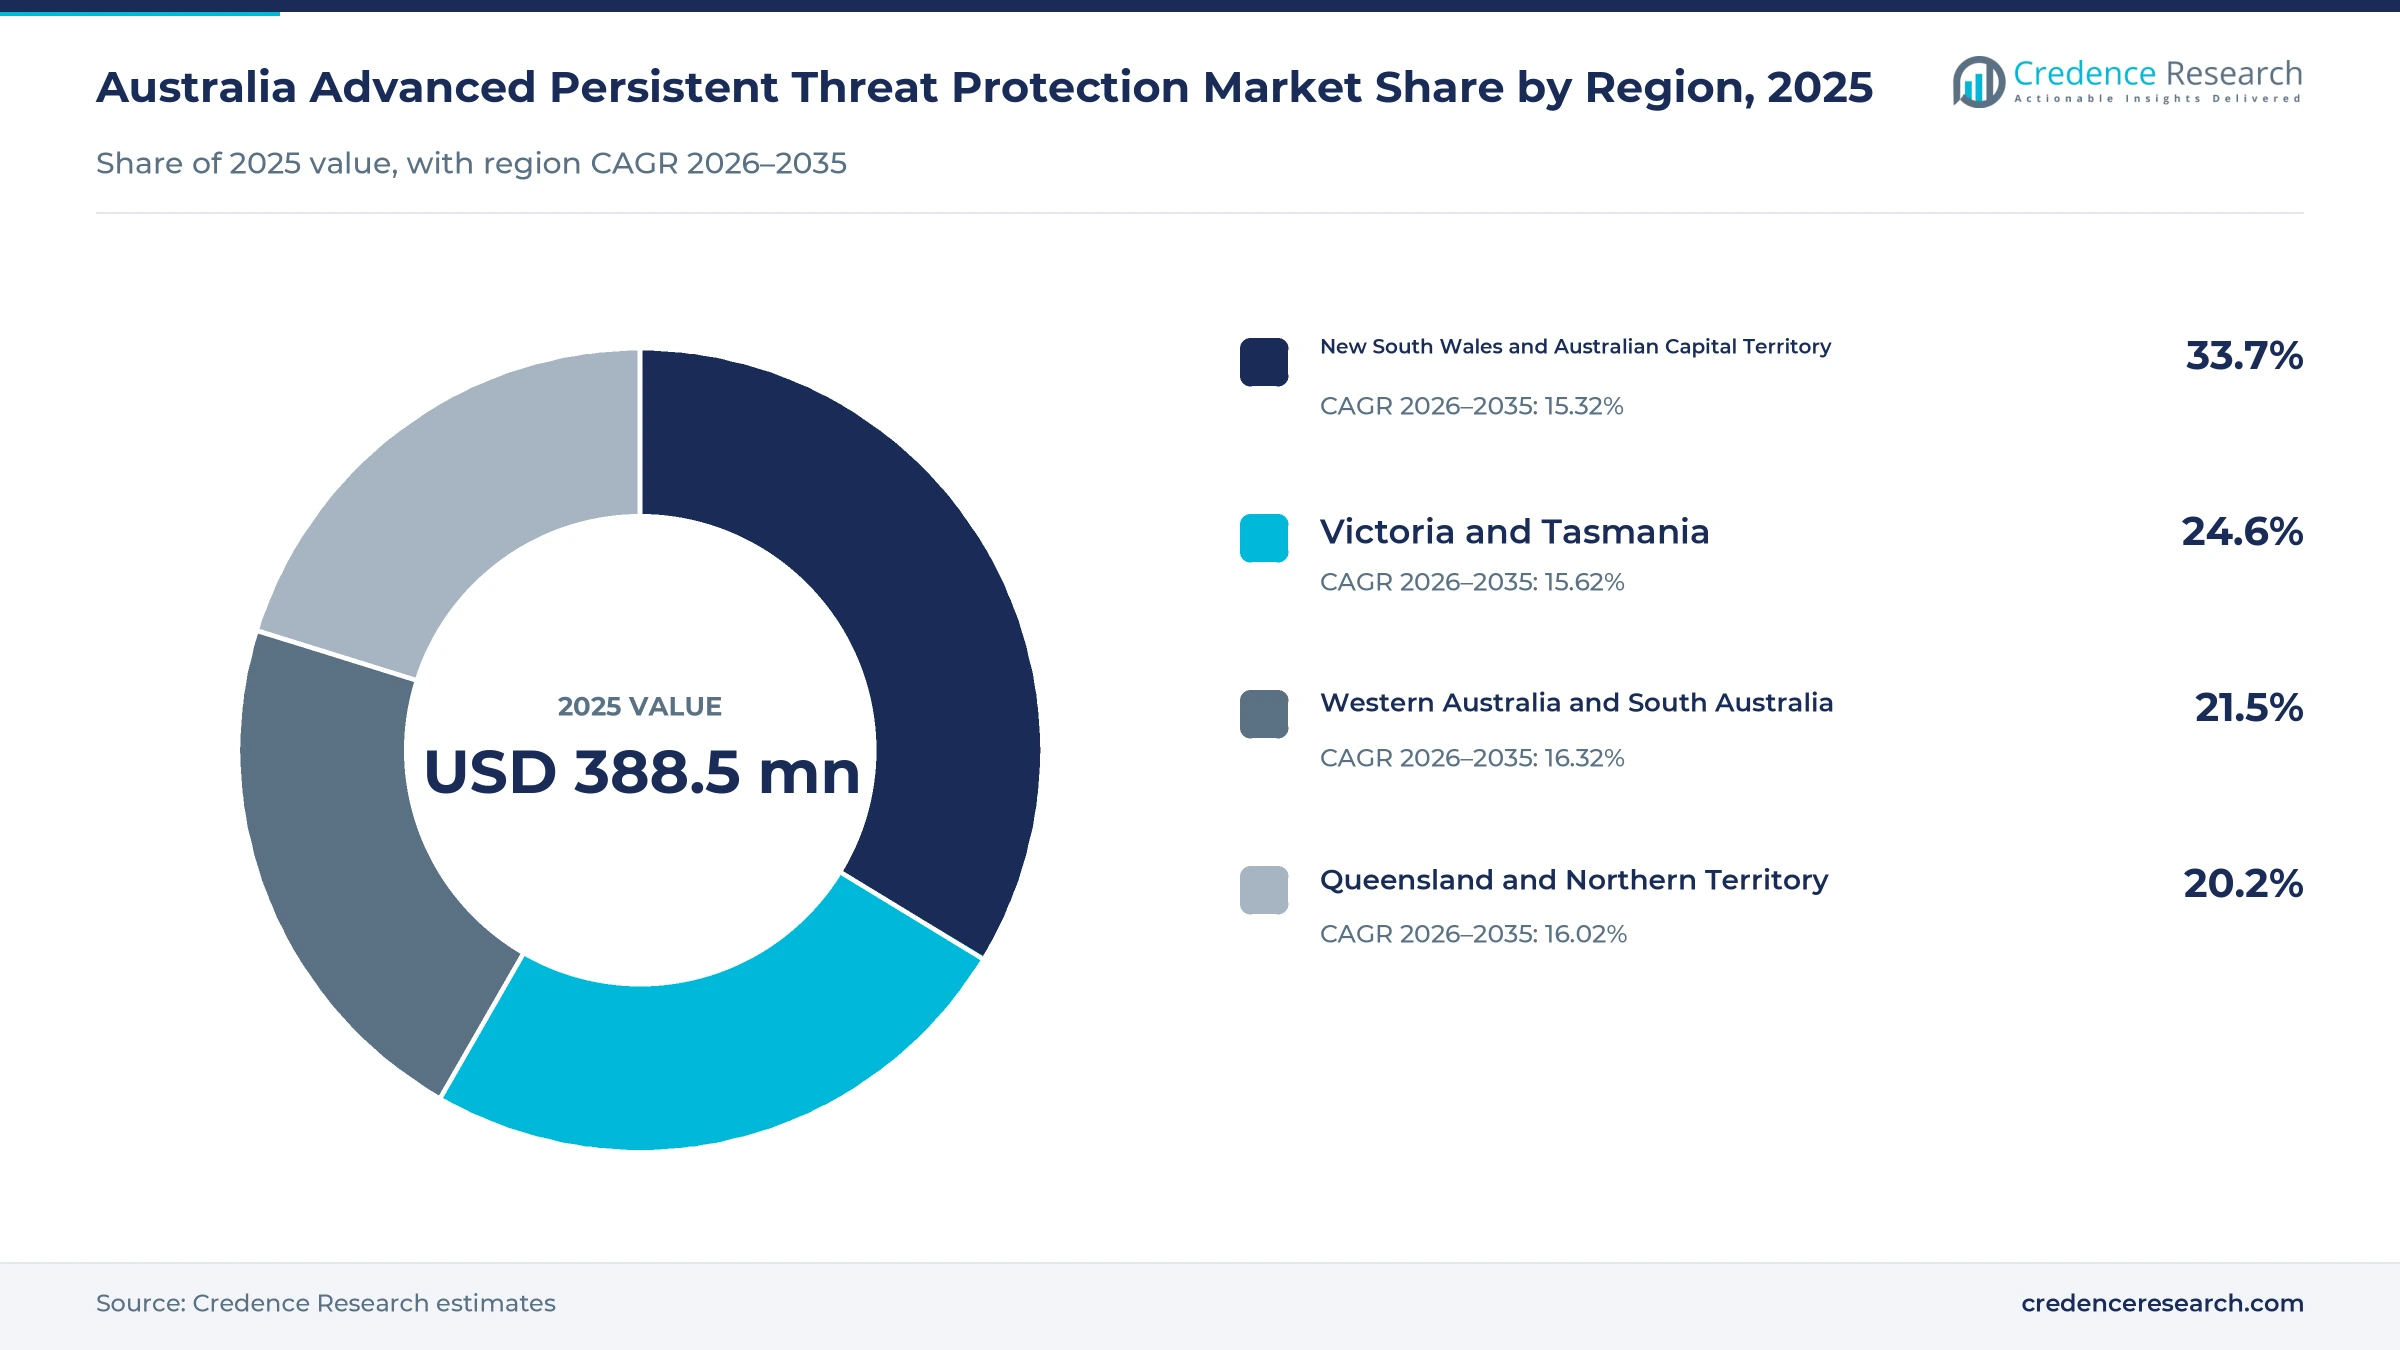
- New South Wales and Australian Capital Territory held a 33.7% share of 2025 value, because Sydney banks and Canberra agencies run the largest monitored estates.
- Endpoint detection platforms led with a 32.0% share of 2025 value, because laptops, servers and cloud workloads are where hidden intruders are most often found.
- The Cyber Security Act 2024 received Royal Assent on Nov. 29, 2024, and its ransomware payment reporting rules have applied since May 30, 2025.
- Accenture announced on Aug. 15, 2025, that it would acquire Melbourne-founded CyberCX, adding about 1,400 security professionals and local operations centers.
Endpoint platforms lead while analytics grows fastest
Why do endpoint detection platforms hold the largest value?
Based on solution type, the market is categorized into endpoint detection platforms, network protection platforms, security analytics platforms and specialist security services. Endpoint Detection Platforms led with a 32.0% share of 2025 value, because laptops, servers and cloud workloads show the first signs of a hidden intruder. Security Analytics Platforms grow fastest at 16.53% a year, as buyers need to link endpoint, network and cloud records to spot quiet movement.
How does cloud hosting change the way buyers deploy?
Based on deployment model, the market is categorized into cloud-hosted, on-premises and hybrid systems. Cloud-Hosted led with a 46.0% share of 2025 value and also grows fastest at 16.52% a year, because vendors now host detection platforms and logs inside Australia. On-premises systems stay important in classified, defense and operational technology networks, where data cannot leave the site.
Which end-use industries spend the most on detection?
Based on end-use industry, the market is categorized into financial services, government and defense, infrastructure and resources, and health, education and enterprise services. Financial Services led with a 29.0% share of 2025 value, because prudential standards hold boards accountable for cyber resilience. Infrastructure and Resources grows fastest at 16.57% a year, as energy, water, port and mining operators face strict incident reporting deadlines.
Why is continuous detection the fastest application?
Based on application, the market is categorized into intrusion prevention, continuous detection, investigation and response, and readiness and assurance. Intrusion Prevention led with a 31.0% share of 2025 value, because firewalls and endpoint blocking remain the first line of defense. Continuous Detection grows fastest at 16.42% a year, as intruders that use built-in tools can only be found by watching behavior around the clock.
| Segment Group | Leading Sub-segment | Share, 2025 | Fastest-growing Sub-segment | CAGR, 2026–2035 |
|---|---|---|---|---|
| By Solution Type | Endpoint Detection Platforms | 32.0% | Security Analytics Platforms | 16.53% |
| By Deployment Model | Cloud-Hosted | 46.0% | Cloud-Hosted | 16.52% |
| By End-Use Industry | Financial Services | 29.0% | Infrastructure and Resources | 16.57% |
| By Application | Intrusion Prevention | 31.0% | Continuous Detection | 16.42% |
Request a Free Sample
Fill in your details and we'll send you a free sample report.
- Sample data tables & charts
- Research methodology
Reporting rules, state actors and APRA standards lift spend
How do critical-infrastructure response obligations lift demand?
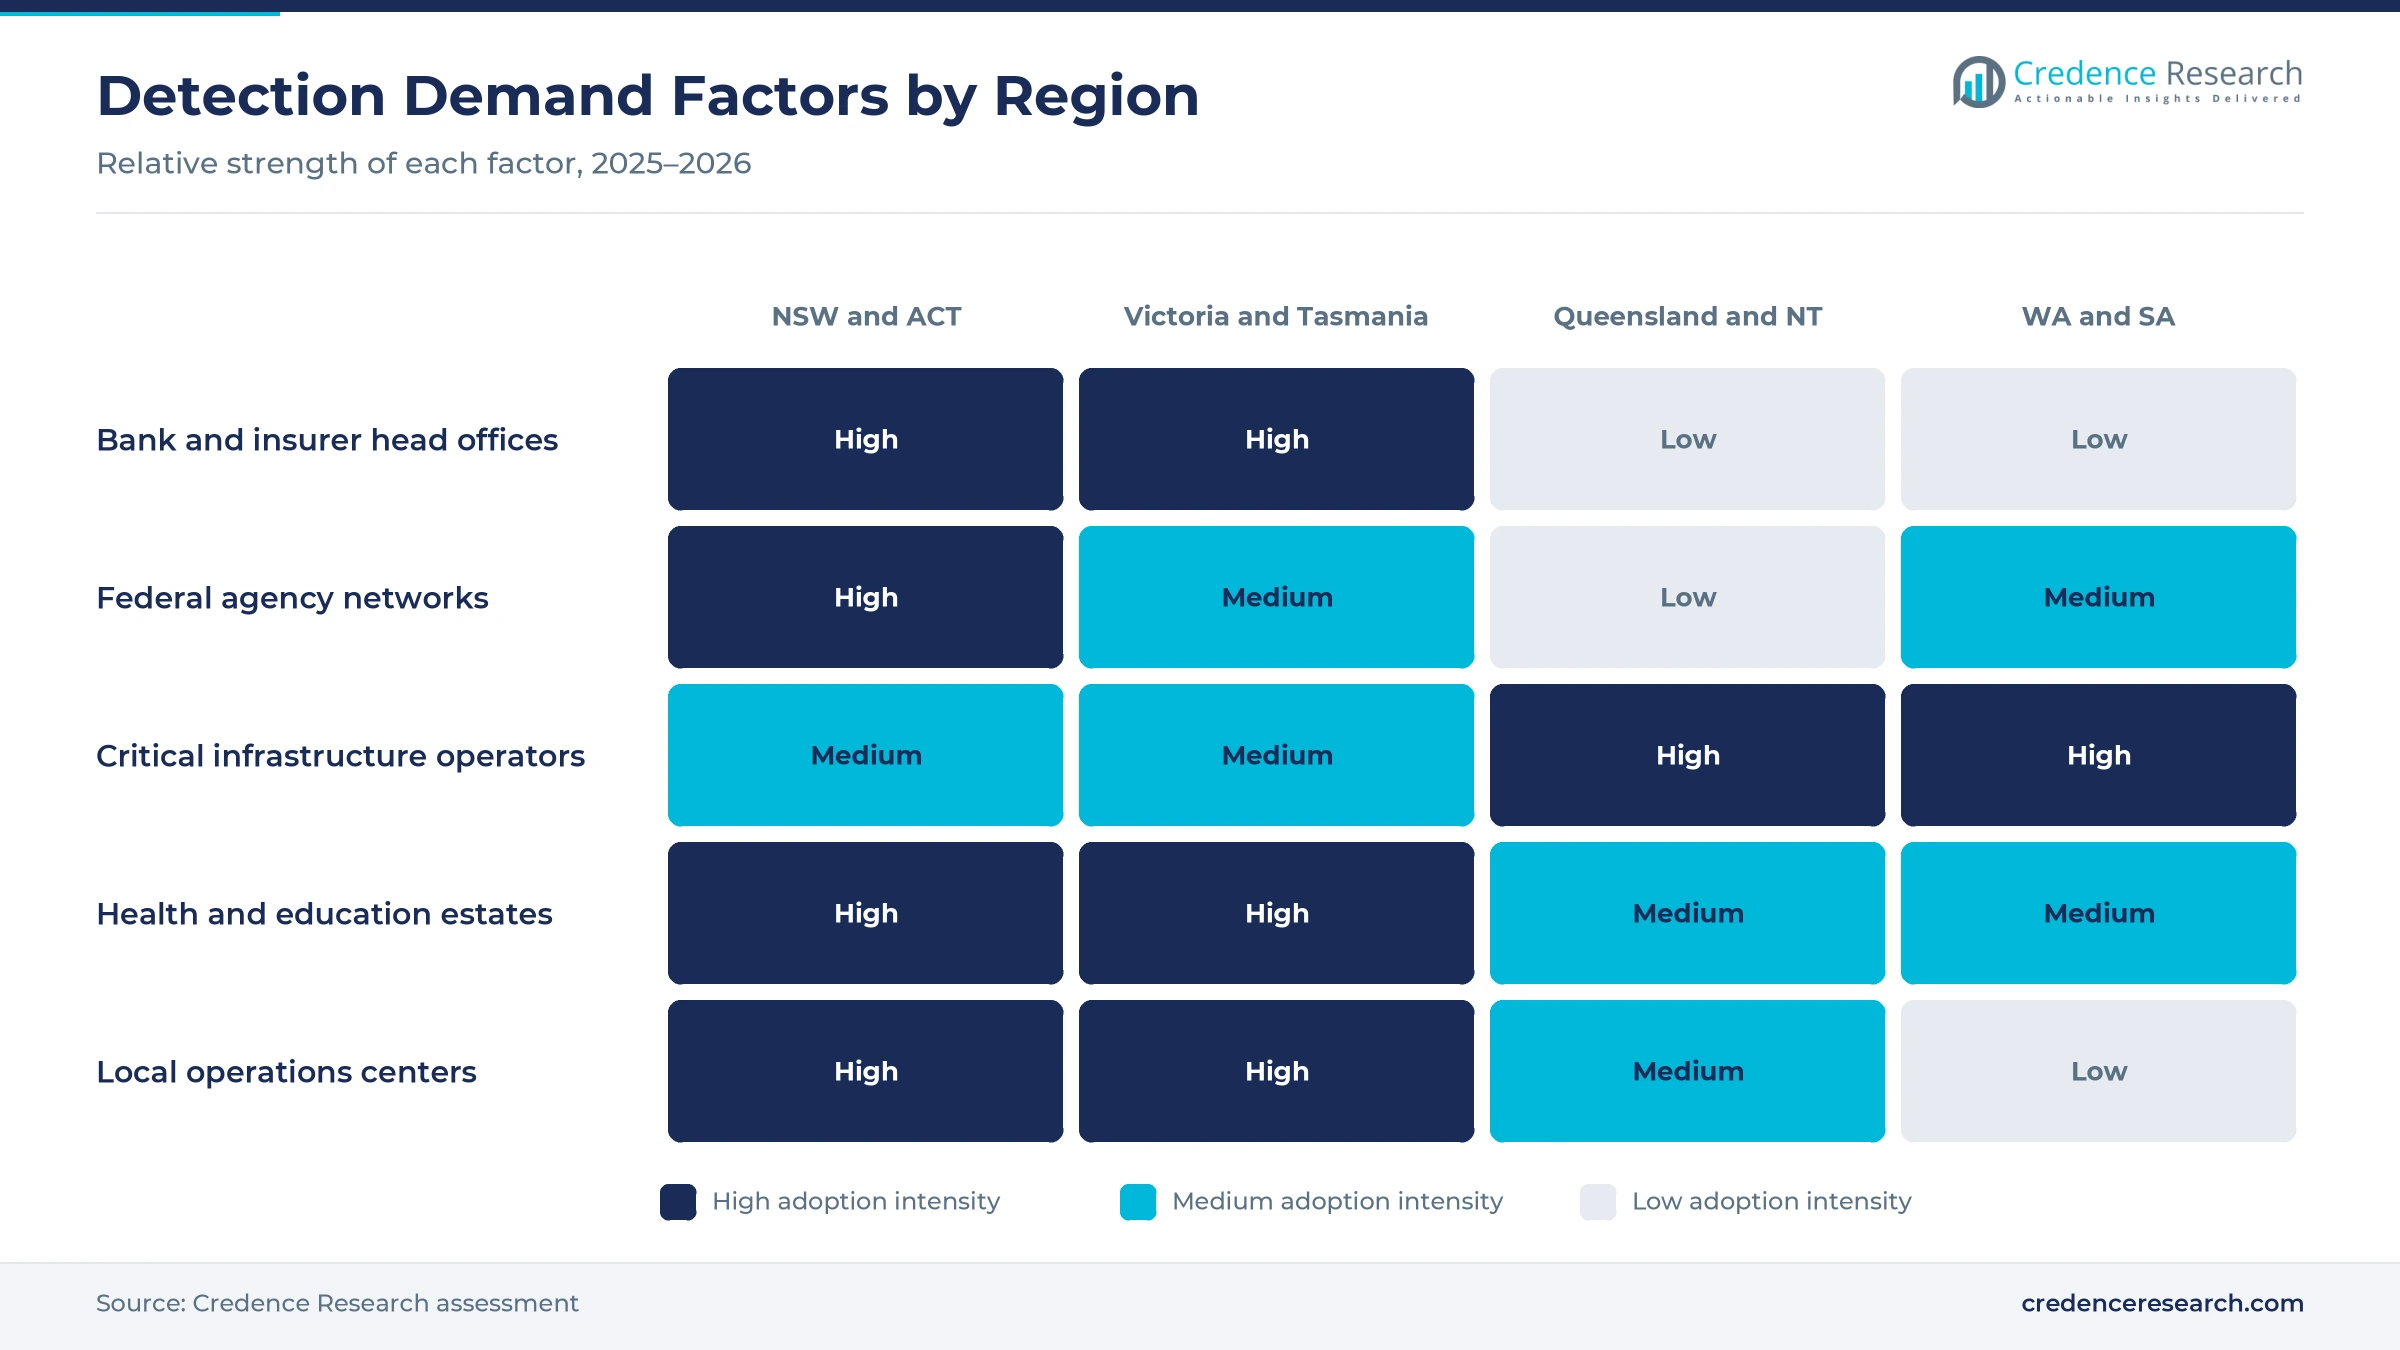
Fixed reporting deadlines force infrastructure operators to detect serious intrusions within hours rather than weeks. Responsible entities must report critical cyber incidents within 12 hours and other reportable incidents within 72 hours, according to the Cyber and Infrastructure Security Centre. The Cyber Security Act 2024 received Royal Assent on Nov. 29, 2024, and its ransomware payment reporting rules started on May 30, 2025, according to the Department of Home Affairs. The Australian Signals Directorate also reports that critical infrastructure made up 13% of the incidents it handled in 2024–25, a higher share than in the year before. As a result, infrastructure and resources buyers grow at 16.57% a year, the fastest end-use industry during 2026–2035.
Why does persistent intrusion exposure keep spending high?
State-sponsored groups aim to stay hidden inside Australian networks for long periods, which keeps budgets for discovery and removal high. The Australian Signals Directorate published its APT40 advisory on July 9, 2024, warning that the group regularly scans networks of interest in Australia and exploits unpatched or end-of-life devices. Its 2024–25 critical infrastructure factsheet says state actors use built-in network tools, known as living off the land, to avoid detection. The agency responded to more than 1,200 incidents in 2024–25, an 11% rise on the year before. Australia also had about 44,299 secure internet servers per million people in 2024, according to World Bank data, which widens the surface to monitor. In turn, endpoint detection platforms hold 32.0% of 2025 value.
How does financial-sector security accountability shape spending?
Boards of banks, insurers and superannuation funds answer directly to the prudential regulator for cyber resilience, which shapes how they buy security. The Australian Prudential Regulation Authority finalized its CPS 234 information security standard on Nov. 7, 2018, and expected all regulated entities to meet it by July 1, 2019. Its CPS 230 operational risk standard has applied to banks, insurers and superannuation funds since July 1, 2025, and requires notice of operational risk incidents. Financial and insurance services accounted for 32% of critical infrastructure incidents handled by the Australian Signals Directorate in 2024–25. As a result, financial services hold 29.0% of 2025 value, the largest end-use share, because banks buy detection, response retainers and regular control testing together.
Why do rising compromise costs favor continuous detection?
A late discovery now carries a much higher bill for larger organizations, which favors monitoring that never pauses. The average self-reported cost of cybercrime for large businesses rose 219% to A$202,700 in 2024–25, according to the Australian Signals Directorate. Medium businesses reported an average of A$97,200, up 55%, while the overall business average rose 50% to A$80,850. Qantas detected unusual activity on a third-party customer servicing platform on June 30, 2025, and later confirmed that data for about 5.7 million customers was compromised. In turn, continuous detection grows at 16.42% a year, the fastest application during 2026–2035, as buyers move from periodic checks to monitoring around the clock.
Onshore security clouds and service consolidation rise
How is the shift to onshore security clouds changing purchases?
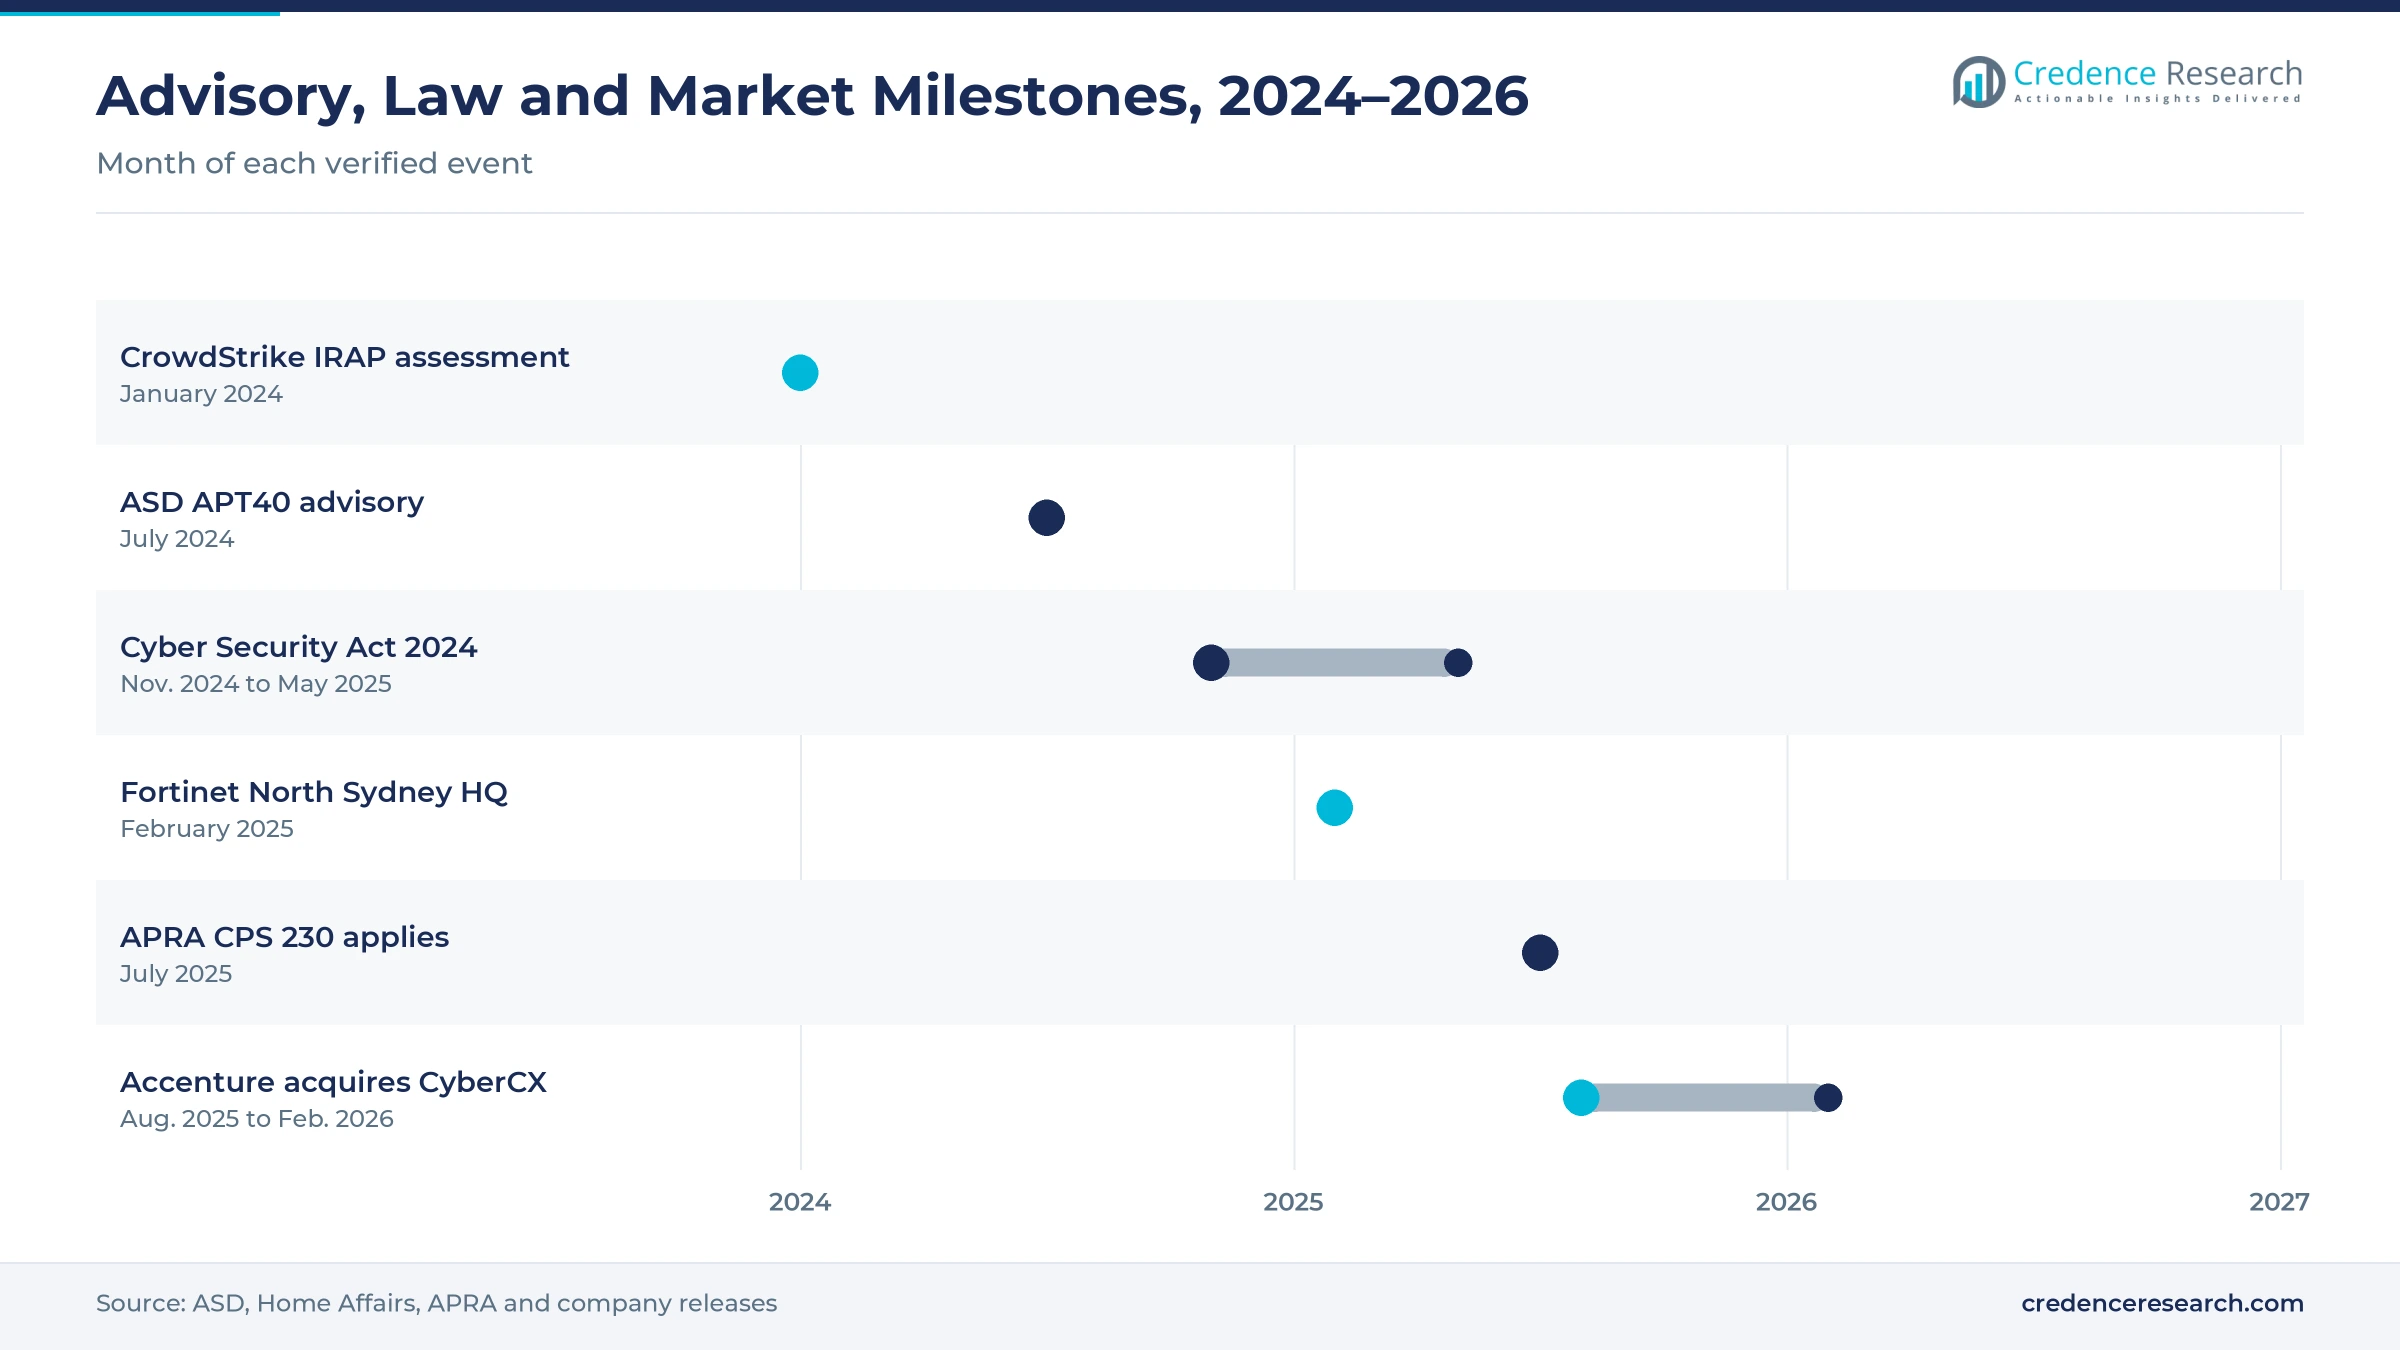
Government and regulated buyers increasingly want telemetry and logs to stay in Australia, which favors vendors with local hosting. Fortinet opened a North Sydney headquarters in February 2025 with an investment of more than AUD 75 million, including a data center for in-region sovereign hosting. CrowdStrike said on Jan. 17, 2024, that its Falcon platform had completed an IRAP assessment, which lets Australian Government customers check its controls against the Information Security Manual. Microsoft announced in October 2023 that it would expand from 20 to 29 local data centers across Canberra, Sydney and Melbourne. As a result, cloud-hosted deployment holds 46.0% of 2025 value and grows at 16.52% a year during 2026–2035.
Why is the rise of services-led consolidation notable?
Many buyers now prefer one partner to run detection, response and recovery across several tools and vendors. Accenture announced on Aug. 15, 2025, that it would acquire Melbourne-founded CyberCX, which it called its largest cyber security acquisition to date. CyberCX brought about 1,400 cyber security professionals and security operations centers across Australia and New Zealand, and the deal closed on Feb. 27, 2026. CyberCX also lists partnerships with Microsoft, Palo Alto Networks and CrowdStrike, which links global platforms to local response teams. In turn, specialist security services gain share during 2026–2035, as buyers rely on managed security services for coverage at night and on weekends.
Can Commonwealth Essential Eight gaps open new demand?
Many federal agencies still fall short of the baseline controls they are directed to meet, which leaves a large uplift program ahead. The Australian Signals Directorate found that only 15% of entities met Maturity Level 2 in its 2024 posture report, down from 25% in 2023. The same report found that 71% of entities said legacy technology affected their ability to implement the Essential Eight, up from 52%. Australian Government entities reported 406 incidents in 2023–24, or 36% of all incidents the Australian Signals Directorate responded to. The 2023–2030 Australian Cyber Security Strategy, released on Nov. 22, 2023, committed A$586.9 million, including A$143.6 million for critical infrastructure and government security. As a result, government and defense buyers have room to fund zero trust architecture and readiness work.
Is there room to grow in health and education security?
Health providers, schools and service firms hold sensitive personal data yet often run small security teams with limited budgets. The Office of the Australian Information Commissioner received 1,205 data breach notifications in 2025, an 8% rise on 2024 and an all-time high. Malicious or criminal attacks caused 716 of those notifications, which is about 59% of the total. Health service providers reported 225 breaches, or 19%, making them the most affected sector for the year, while financial services reported 157. In turn, providers that package endpoint detection and response tools with monitoring can reach health and education buyers with small security teams.
Skills gaps, legacy systems and supplier risk slow uptake
How do security skills shortages slow adoption?
Threat hunting and incident response need experienced analysts who are hard to hire outside Sydney, Melbourne and Canberra. As a result, many mid-sized organizations buy detection tools but lack staff to act on alerts at night. Providers respond with managed detection retainers and shared operations centers, which spread scarce analysts across many clients. This shortage stays tight while banks, agencies and infrastructure operators compete for the same people.
Why do legacy systems make detection harder?
Old devices often cannot run modern agents or send useful logs to analytics platforms, which leaves blind spots in many networks. The Australian Signals Directorate found that 71% of Commonwealth entities said legacy technology hurt their Essential Eight work in 2024. In turn, intruders can hide on unpatched or end-of-life equipment, as the APT40 advisory warned. Buyers respond with network sensors and replacement programs, which add cost and time before full coverage is reached.
How does third-party exposure complicate protection?
Attackers can reach customer data through suppliers, call centers and software platforms outside the main network. The Qantas incident in mid-2025 began on a third-party customer servicing platform rather than on the airline's core systems. As a result, buyers must extend monitoring and contract controls to vendors they do not run. Regulators now expect boards to manage material service providers, which adds assurance work for every major contract.
Why do costs weigh on smaller organizations?
Full detection platforms, logging and retainers can exceed the budget of a firm with fewer than 200 employees. The average self-reported cybercrime cost for a small business still reached A$56,600 in 2024–25, which shows the risk is real for these buyers. Providers respond with consumption-based subscriptions and bundled monitoring, which lower entry costs. However, many small firms still rely on basic controls rather than continuous detection.
Sydney and Canberra lead while the west grows fastest
| Region | Value, 2025 (USD million) | Share, 2025 | CAGR, 2026–2035 |
|---|---|---|---|
| New South Wales and Australian Capital Territory | 130.9 | 33.7% | 15.32% |
| Victoria and Tasmania | 95.6 | 24.6% | 15.62% |
| Western Australia and South Australia | 83.5 | 21.5% | 16.32% |
| Queensland and Northern Territory | 78.5 | 20.2% | 16.02% |
Why do New South Wales and the ACT hold the top share?
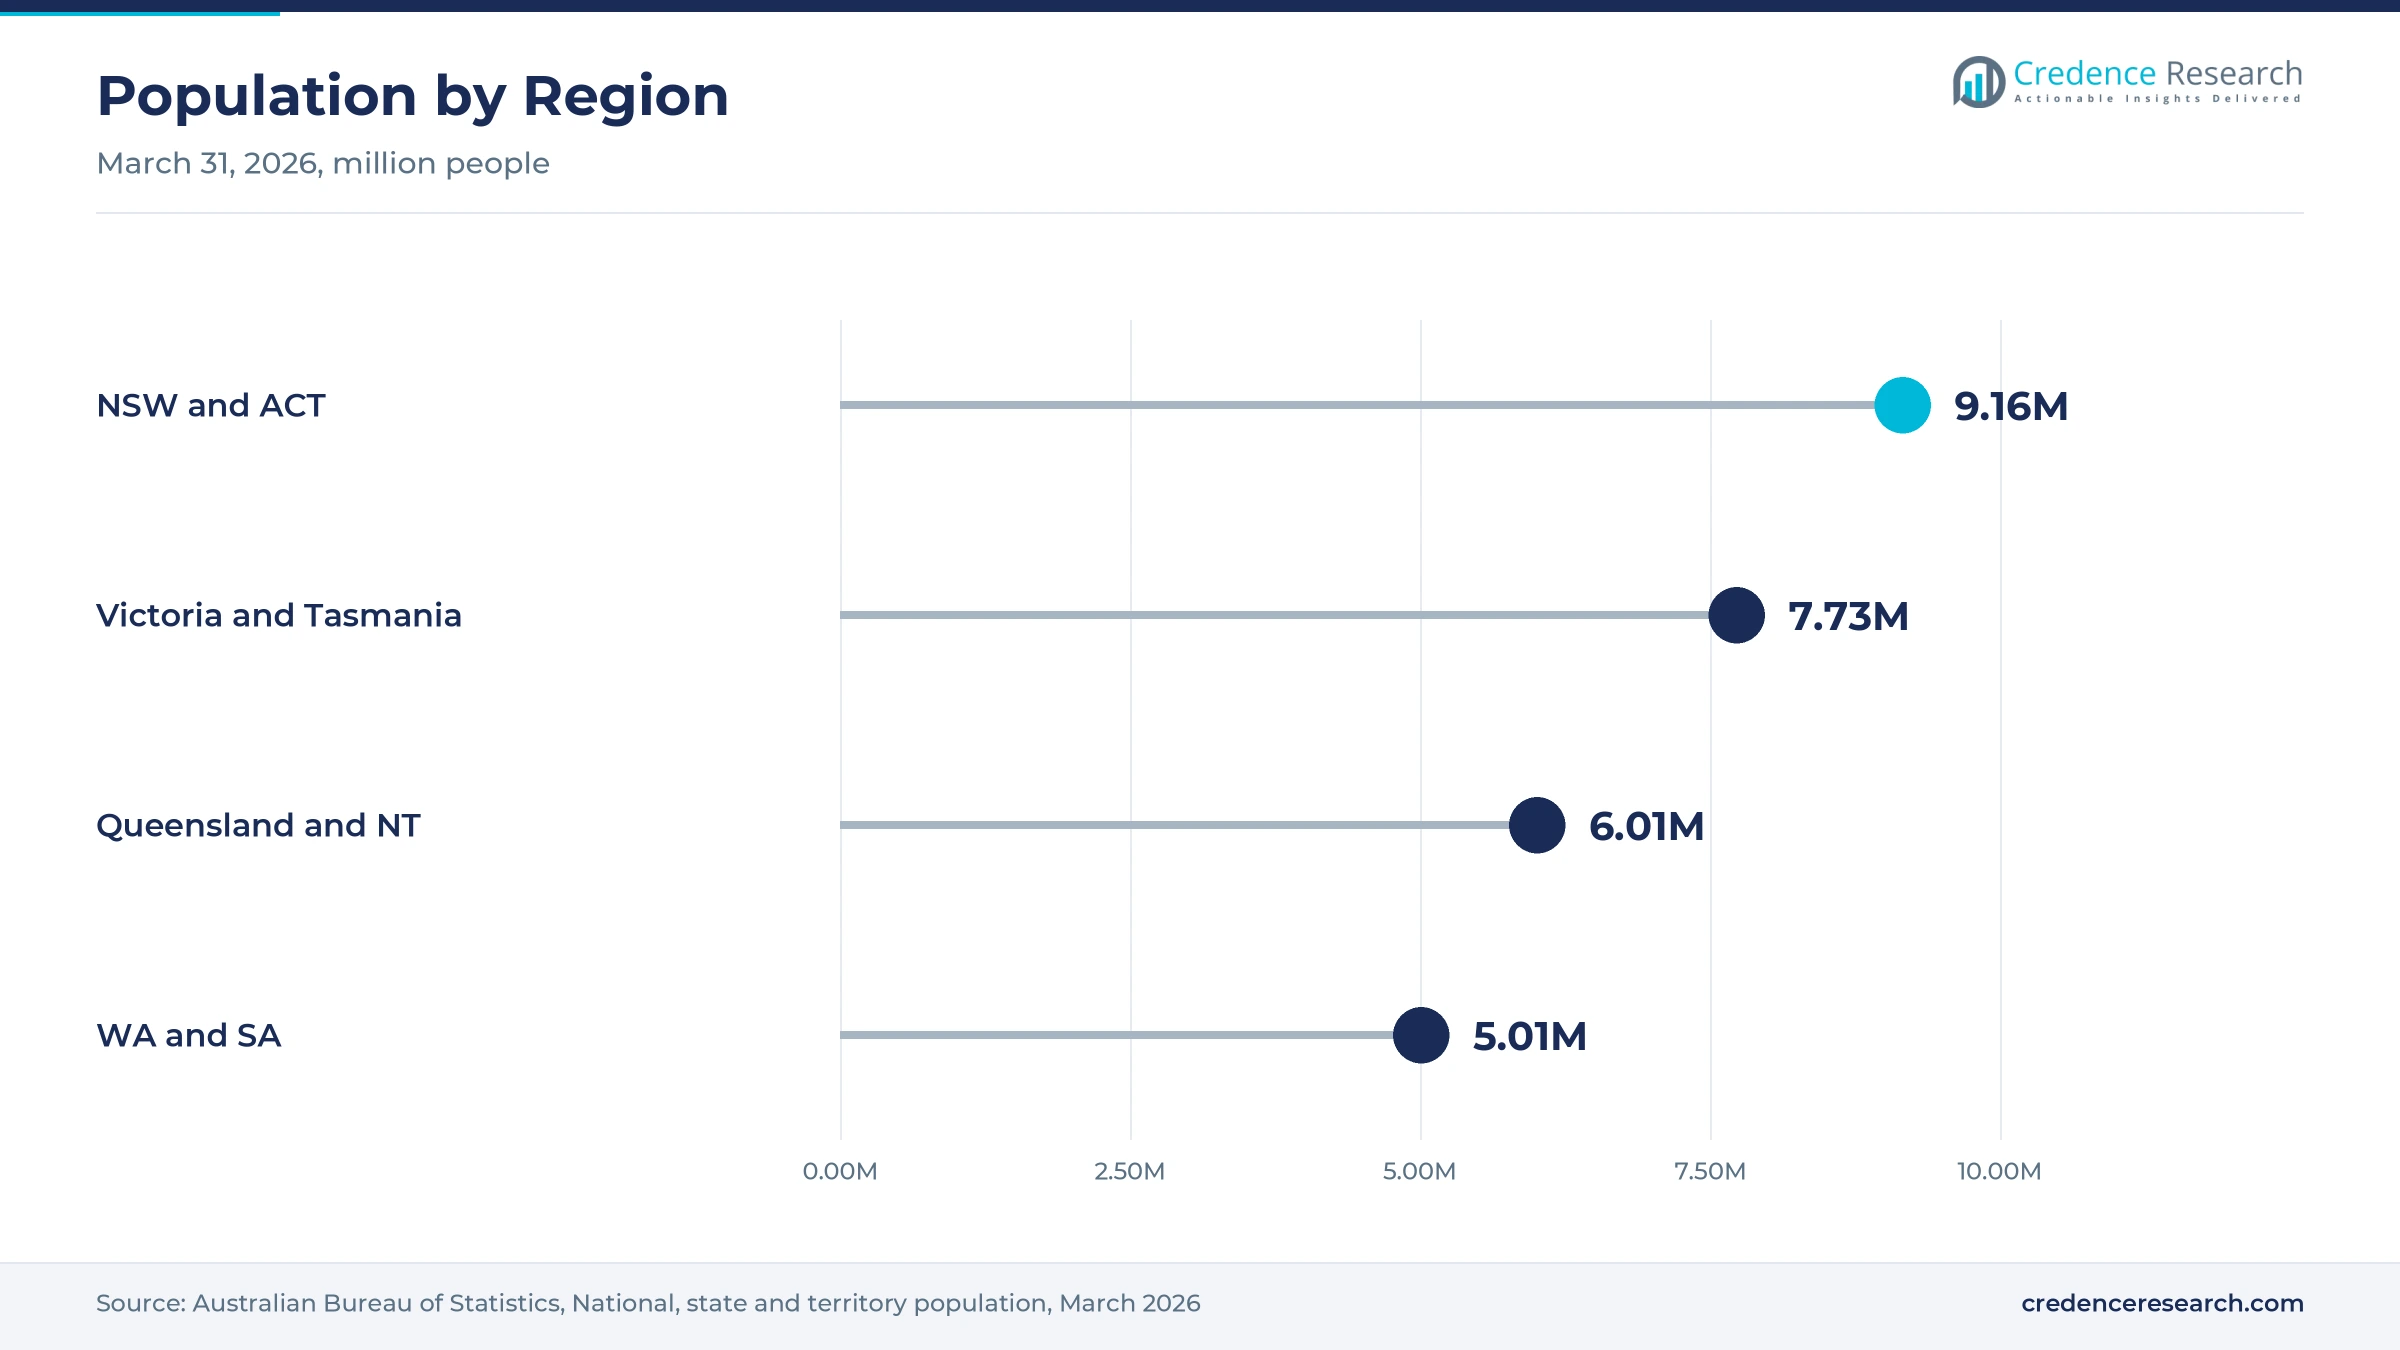
New South Wales and Australian Capital Territory held a 33.7% share of 2025 value and grow at 15.32% a year, because Sydney hosts most bank and insurer head offices while Canberra concentrates federal agencies. The zone had about 9.16 million residents in March 2026, according to Australian Bureau of Statistics data. Fortinet runs its national headquarters in North Sydney, and Microsoft operates data centers in both cities. As a result, this zone buys the largest volume of platforms and response retainers.
How do Victoria and Tasmania support demand?
Victoria and Tasmania held a 24.6% share of 2025 value and grow at 15.62% a year, because Melbourne combines insurers, superannuation funds, universities and health networks. The zone had about 7.73 million residents in March 2026, and Victoria grew 1.6% over the previous year. CyberCX was founded in Melbourne in 2019 and runs security operations centers across Australia and New Zealand. In turn, the zone holds the second largest regional share of detection and response spending.
Why are Western Australia and South Australia growing fastest?
Western Australia and South Australia held a 21.5% share of 2025 value and grow fastest at 16.32% a year, because mining, energy and defense operators are adding monitoring to operational networks. Western Australia had the fastest population growth of any state, 2.1% over the year to March 2026. Infrastructure operators in both states must meet the 12-hour reporting deadline for critical incidents. As a result, this zone buys more hybrid systems and operational technology monitoring.
How do Queensland and the Northern Territory contribute?
Queensland and Northern Territory held a 20.2% share of 2025 value and grow at 16.02% a year, because ports, power networks, resources and state agencies need stronger detection. The zone had about 6.01 million residents in March 2026, and Queensland grew 1.6% over the previous year. Many infrastructure owners in the zone run remote sites with limited local security staff. In turn, Queensland and Northern Territory buyers favor cloud-hosted platforms with managed monitoring.
Advisories, new laws and a major services acquisition
| Development | Status and market relevance |
|---|---|
| In January 2024, CrowdStrike said its Falcon platform had completed an IRAP assessment for Australian Government use. | Opens endpoint detection sales to agencies that require assessed services |
| In July 2024, the Australian Signals Directorate published its APT40 advisory on state-sponsored intrusion tradecraft. | Highlights stealthy access through unpatched and end-of-life devices |
| In November 2024, the Cyber Security Act 2024 received Royal Assent and became law. | Ransomware payment reporting applies from May 30, 2025 |
| In February 2025, Fortinet opened its North Sydney headquarters with in-region sovereign hosting. | Adds local hosting, a technical assistance center and training space |
| In August 2025, Accenture announced its acquisition of CyberCX, which closed in February 2026. | Combines a global services firm with local operations centers |
Endpoint telemetry, analytics and shared intelligence
- Endpoint telemetry records process, file and login activity on every device, which lets analysts spot tools that intruders run quietly.
- Network detection and firewalls watch traffic between sites, clouds and partners, which helps block scanning and catch data leaving the network.
- Security analytics platforms combine logs from endpoints, networks, identity and cloud services, which reveals slow movement that single tools miss.
- Shared threat intelligence moves millions of indicators of compromise from the Australian Signals Directorate network to hundreds of Australian partners, which speeds up the blocking of known attackers.
Need a Custom Version of This Report?
Tailor the scope, geography, or segments to your exact requirements.
- Custom geography or segment scope
- Direct access to our analyst team
Global platforms and local responders compete on trust
Competition combines global platform vendors with local service firms that run detection and response around the clock. CrowdStrike sells its Falcon endpoint platform to Australian agencies after completing an IRAP assessment in January 2024. Palo Alto Networks serves Cortex XDR and Cortex Data Lake from an Australian cloud location that opened in January 2021, which keeps customer logs onshore. Fortinet runs a North Sydney headquarters with more than 200 staff, a technical assistance center and sovereign hosting. Microsoft works with the Australian Signals Directorate on the Microsoft-ASD Cyber Shield while expanding its local data centers. Accenture, through CyberCX, adds about 1,400 professionals and local security operations centers. Many buyers combine XDR platforms from one vendor with response retainers from another, so integration skill matters. Vendors compete on local hosting, government assessments, response speed and intelligence depth.
Which vendors and service firms lead Australian detection work?
| Company | Type | Role in the market |
|---|---|---|
| Accenture / CyberCX | Security services provider | Runs operations centers across Australia and New Zealand |
| CrowdStrike | Endpoint platform vendor | Falcon platform completed IRAP assessment in January 2024 |
| Palo Alto Networks | Platform vendor | Hosts Cortex XDR and Cortex Data Lake in Australia |
| Fortinet | Network security vendor | Opened North Sydney headquarters with sovereign hosting |
| Microsoft | Cloud and security vendor | Builds the Microsoft-ASD Cyber Shield with the agency |
Credence Research view on detection and response demand
Credence Research's view is that Australian spending on detection and response will grow quickly because reporting deadlines, state-sponsored intrusions and prudential standards all reward faster discovery. Endpoint detection platforms remain the largest solution type, while security analytics platforms grow fastest as buyers join endpoint, network and cloud records. Western Australia and South Australia gain most from operational network monitoring, while Sydney and Canberra keep the largest installed bases. Vendors that combine onshore hosting, government assessments and local response teams should gain the most share by 2035.
How the national detection and response estimate was built
The report uses 2025 as the base year on a calendar basis, and market values come from the Credence Research model. That model combines regulator guidance, government threat reports, official population and internet statistics, privacy regulator data and company releases. Regional shares, regional growth rates and segment splits are Credence Research estimates built from population and incident data. Sources used are government and regulator pages, World Bank data, trade media and company websites, and no interviews or surveys were used.
Infrastructure, cloud and detection carry growth to 2035
The Australia advanced persistent threat protection market is expected to reach USD 1.71 billion by 2035, a 15.76% CAGR during 2026–2035, as agencies, banks and infrastructure operators keep investing in faster discovery and response. Growth should be strongest in security analytics, cloud-hosted deployment, continuous detection and infrastructure buyers, because these areas gain most from reporting deadlines and stealthy intrusions. Skills shortages, legacy systems and supplier exposure could slow some programs, while managed services and onshore hosting should widen access for mid-sized and smaller organizations.
Frequently Asked Questions
How big is the Australia advanced persistent threat protection market?
Which solution type leads spending?
Which region leads the market?
How do incident reporting rules affect demand?
Why are state-sponsored intrusions a concern in Australia?
How do APRA standards affect financial institutions?
Who are the leading companies in Australian detection and response?
What are the main challenges for buyers?
Table of Content
Chapter 1 Market Segmentation
- 1.1 Segmentation Framework
- 1.1.1 Product and Service Classification
- 1.1.2 Application and End-Use Classification
- 1.1.3 Technology and Solution Classification
- 1.1.4 Customer and Distribution Channel Classification
- 1.1.5 Geographic Segmentation
- 1.1.6 Market Segment Definitions and Boundaries
- 1.2 By Solution Type
- 1.2.1 Endpoint Detection Platforms
- 1.2.2 Network Protection Platforms
- 1.2.3 Security Analytics Platforms
- 1.2.4 Specialist Security Services
- 1.3 By Deployment Model
- 1.3.1 Cloud-Hosted
- 1.3.2 On-Premises
- 1.3.3 Hybrid
- 1.4 By End-Use Industry
- 1.4.1 Financial Services
- 1.4.2 Government and Defence
- 1.4.3 Infrastructure and Resources
- 1.4.4 Health, Education and Enterprise Services
- 1.5 By Application
- 1.5.1 Intrusion Prevention
- 1.5.2 Continuous Detection
- 1.5.3 Investigation and Response
- 1.5.4 Readiness and Assurance
Chapter 2 Introduction
- 2.1 Report Objectives and Scope
- 2.2 Product Definition and Industry Terminology
- 2.3 Market Inclusions and Exclusions
- 2.4 Research Process
- 2.4.1 Primary Research and Expert Interviews
- 2.4.2 Secondary Research and Source Review
- 2.4.3 Top-Down and Bottom-Up Estimation
- 2.4.4 Data Triangulation and Verification
- 2.5 Market Size Measurement Basis
- 2.5.1 2025: USD 388.5 million → 2035: USD 1.71 billion
- 2.6 Historical and Forecast Reference Periods
- 2.6.1 Historical Period: 2018-2025
- 2.6.2 Base Year: 2025
- 2.6.3 Forecast Period: 2025-2035
- 2.7 Research Assumptions and Limitations
Chapter 3 Executive Summary
- 3.1 Market Snapshot and Key Findings
- 3.2 Base-Year Market Size, 2025
- 3.3 Forecast Market Size, 2035
- 3.4 Revenue and Volume Growth Outlook
- 3.5 Key Demand and Supply Indicators
- 3.6 Leading Market Segments
- 3.7 Fastest-Growing Market Opportunities
- 3.8 Regional Performance Highlights
- 3.9 Technology and Industry Transformation
- 3.10 Competitive Landscape Summary
- 3.11 Analyst View and Strategic Implications
Chapter 4 Australia Advanced Persistent Threat Protection Market Trends and Developments
- 4.1 Historical Industry Development, 2018-2025
- 4.2 Recent Market Trends and Developments
- 4.3 Demand and Customer Behavior Trends
- 4.4 Technology and Product Innovation
- 4.5 Artificial Intelligence, Automation and Digitalization
- 4.6 Local Manufacturing and Supply Chain Realignment
- 4.7 Industry Partnerships, Mergers and Acquisitions
- 4.8 Sustainability and Circular Economy Developments
- 4.9 Government and Private Sector Investment Trends
- 4.10 Emerging Business Models and Commercialization
- 4.11 Industry Developments and Announcements
Chapter 5 Australia Advanced Persistent Threat Protection Market Supply and Demand Analysis
- 5.1 Demand Trend and Consumption Analysis, 2018-2025
- 5.2 Demand Forecast, 2025-2035
- 5.3 Supply Chain Structure and Procurement Trends
- 5.4 Supply-Demand Gap and Bottlenecks
- 5.5 Import Dependence and Sourcing Structure
- 5.6 Regional Supply and Demand Concentration
Chapter 6 Australia Advanced Persistent Threat Protection Market Pricing Analysis
- 6.1 Pricing Structure and Measurement
- 6.2 Historical Pricing Trends, 2018-2025
- 6.3 Pricing Outlook, 2025-2035
- 6.4 Pricing by Product and Market Segment
- 6.5 Geographic Pricing Differences
- 6.6 Key Input, Energy, Labor and Logistics Costs
- 6.7 Contract Pricing and Purchasing Models
- 6.8 Pricing Sensitivity and Competitive Positioning
- 6.9 Price, Margin and Profitability Implications
Chapter 7 Australia Advanced Persistent Threat Protection Market Dynamics
- 7.1 Market Growth Drivers
- 7.1.1 Demand-Side Drivers
- 7.1.2 Technology and Innovation Drivers
- 7.1.3 Infrastructure and Investment Drivers
- 7.1.4 Regulatory and Policy Drivers
- 7.2 Market Restraints
- 7.2.1 Cost and Affordability Constraints
- 7.2.2 Technology and Adoption Barriers
- 7.2.3 Supply Chain and Operational Constraints
- 7.3 Market Challenges
- 7.3.1 Competitive Pressure and Margin Erosion
- 7.3.2 Skills, Infrastructure and Implementation Gaps
- 7.4 Emerging Market Opportunities
- 7.5 Market Dynamics Impact and Time-Horizon Assessment
Chapter 8 Australia Advanced Persistent Threat Protection Value Chain Analysis
- 8.1 Industry Value Chain Overview
- 8.2 Upstream Suppliers and Critical Inputs
- 8.3 Technology and Component Providers
- 8.4 Manufacturing or Service Delivery
- 8.5 Distribution, Channel Partners and Integrators
- 8.6 Downstream Applications and End Users
- 8.7 Value Addition and Profit Pools
- 8.8 Vertical Integration and Outsourcing
- 8.9 Supplier Concentration and Risk
- 8.10 Supply Chain Localization and Resilience
Chapter 9 Australia Advanced Persistent Threat Protection Market Regulations and Policies
- 9.1 Relevant Laws, Standards and Compliance Frameworks
- 9.2 Product, Service, Safety and Quality Requirements
- 9.3 Government Policies, Incentives and Subsidies
- 9.4 Imports, Exports and Trade Barriers
- 9.5 Public Procurement and Local Content Requirements
- 9.6 Data Protection, AI and Cybersecurity Compliance
- 9.7 Upcoming Policy Changes and Market Implications
Chapter 10 Australia Advanced Persistent Threat Protection Market Hotspots and Opportunities
- 10.1 Market Opportunity Mapping and Growth Hotspots
- 10.2 High-Growth Applications and Customer Groups
- 10.3 Underserved Markets and White-Space Opportunities
- 10.4 Emerging Technology and Product Opportunities
- 10.5 New Capacity and Investment Hotspots
- 10.6 Market Entry and Expansion Opportunities
- 10.7 Distribution and Partnership Opportunities
- 10.8 Near-Term and Long-Term Commercial Potential
- 10.9 Opportunity Attractiveness and Execution Risks
Chapter 11 Australia Advanced Persistent Threat Protection Market Outlook, 2025-2035
- 11.1 Market Size and Analysis
- 11.1.1 Revenue (Market Measurement: 2025: USD 388.5 million → 2035: USD 1.71 billion)
- 11.1.2 Historical Market Size, 2018-2025
- 11.1.3 Base-Year Market Size, 2025
- 11.2 Market Forecast, 2025-2035
- 11.2.1 Revenue Forecast to 2035
- 11.2.2 CAGR and Year-on-Year Growth
- 11.2.3 Incremental Revenue Opportunity
- 11.3 Forecast Assumptions and Scenario Analysis
- 11.3.1 Base-Case Forecast
- 11.3.2 Optimistic and Conservative Scenarios
- 11.3.3 Technology, Pricing and Policy Sensitivities
- 11.4 Market Attractiveness and Growth Outlook
Chapter 12 Australia Advanced Persistent Threat Protection Market Segmentation and Outlook
- 12.1 Segmentation Summary and Market Shares, 2025
- 12.2 Largest and Fastest-Growing Segments
- 12.3 By Solution Type - Market Size and Forecast, 2025-2035
- 12.3.1 Segment Definition and Scope
- 12.3.2 Historical Market Size, 2018-2025
- 12.3.3 Revenue Forecast, 2025-2035
- 12.3.4 Base-Year Market Share, 2025
- 12.3.5 Segment CAGR and Growth Drivers
- 12.3.6 Subsegment Market Size and Forecast
- 12.3.6.1 Endpoint Detection Platforms
- 12.3.6.2 Network Protection Platforms
- 12.3.6.3 Security Analytics Platforms
- 12.3.6.4 Specialist Security Services
- 12.3.7 Subsegment Pricing and Adoption Trends
- 12.3.8 Leading Suppliers and Competition
- 12.3.9 Regional Demand and Opportunities
- 12.4 By Deployment Model - Market Size and Forecast, 2025-2035
- 12.4.1 Segment Definition and Scope
- 12.4.2 Historical Market Size, 2018-2025
- 12.4.3 Revenue Forecast, 2025-2035
- 12.4.4 Base-Year Market Share, 2025
- 12.4.5 Segment CAGR and Growth Drivers
- 12.4.6 Subsegment Market Size and Forecast
- 12.4.6.1 Cloud-Hosted
- 12.4.6.2 On-Premises
- 12.4.6.3 Hybrid
- 12.4.7 Subsegment Pricing and Adoption Trends
- 12.4.8 Leading Suppliers and Competition
- 12.4.9 Regional Demand and Opportunities
- 12.5 By End-Use Industry - Market Size and Forecast, 2025-2035
- 12.5.1 Segment Definition and Scope
- 12.5.2 Historical Market Size, 2018-2025
- 12.5.3 Revenue Forecast, 2025-2035
- 12.5.4 Base-Year Market Share, 2025
- 12.5.5 Segment CAGR and Growth Drivers
- 12.5.6 Subsegment Market Size and Forecast
- 12.5.6.1 Financial Services
- 12.5.6.2 Government and Defence
- 12.5.6.3 Infrastructure and Resources
- 12.5.6.4 Health, Education and Enterprise Services
- 12.5.7 Subsegment Pricing and Adoption Trends
- 12.5.8 Leading Suppliers and Competition
- 12.5.9 Regional Demand and Opportunities
- 12.6 By Application - Market Size and Forecast, 2025-2035
- 12.6.1 Segment Definition and Scope
- 12.6.2 Historical Market Size, 2018-2025
- 12.6.3 Revenue Forecast, 2025-2035
- 12.6.4 Base-Year Market Share, 2025
- 12.6.5 Segment CAGR and Growth Drivers
- 12.6.6 Subsegment Market Size and Forecast
- 12.6.6.1 Intrusion Prevention
- 12.6.6.2 Continuous Detection
- 12.6.6.3 Investigation and Response
- 12.6.6.4 Readiness and Assurance
- 12.6.7 Subsegment Pricing and Adoption Trends
- 12.6.8 Leading Suppliers and Competition
- 12.6.9 Regional Demand and Opportunities
- 12.7 Segment Growth Comparison
- 12.8 Segment Attractiveness and Priority Matrix
Chapter 13 Australia Advanced Persistent Threat Protection End-Use and Application Market Outlook
- 13.1 End-Use Industry and Customer Demand Structure
- 13.2 Leading Applications and Customer Groups
- 13.3 End-Use Market Size, Share and Forecast
- 13.4 Major End-Use Industry Deep Dives
- 13.4.1 Customer Requirements and Use Cases
- 13.4.2 Demand and Replacement Cycles
- 13.4.3 Technical and Regulatory Considerations
- 13.4.4 Purchasing and Procurement Models
- 13.4.5 Leading Vendors and Distribution Channels
- 13.4.6 Forecast and Commercial Opportunities
- 13.5 Emerging Applications and Cross-Segment Demand
- 13.6 End-Use Industry Investment Priorities
Chapter 14 Australia Advanced Persistent Threat Protection Geographic Market Outlook, 2025-2035
- 14.1 Domestic Market Distribution and Demand Clusters
- 14.2 State- or Province-Wise Market Size and Forecast, 2025-2035
- 14.3 City and Metropolitan Market Outlook
- 14.4 Industrial, Manufacturing and Commercial Clusters
- 14.5 Geographic Concentration of Key End Users
- 14.6 Local Pricing and Purchasing Differences
- 14.7 Domestic Production Facilities and Capacity Map
- 14.8 Local Infrastructure and Project Pipeline
- 14.9 State-Level Policy and Incentive Differences
- 14.10 Subnational Investment Hotspots and Opportunities
- 14.11 Distribution and Logistics Networks
- 14.12 Domestic Competitive Footprint
Chapter 15 Australia Advanced Persistent Threat Protection Technology, Innovation and Sustainability Outlook
- 15.1 Technology Landscape and Maturity
- 15.2 Product, Process and Service Innovation
- 15.3 AI, Automation and Digital Tools in the Industry
- 15.4 Technology Adoption and Performance Benchmarking
- 15.5 Innovation Pipeline and R&D Investment
- 15.6 Patent and Intellectual Property Trends
- 15.7 Energy Efficiency and Resource Management
- 15.8 Sustainability, Recycling and Circularity
- 15.9 Technology Roadmap, 2025-2035
- 15.10 Risks of Obsolescence and Technology Substitution
Chapter 16 Australia Advanced Persistent Threat Protection Market Key Strategic Imperatives
- 16.1 Growth and Market Entry Priorities
- 16.2 High-Return Products and Segments
- 16.3 Pricing, Profitability and Cost Optimization
- 16.4 Technology Investment and Product Differentiation
- 16.5 Supply Chain Localization and Resilience
- 16.6 Distribution and Customer Acquisition
- 16.7 Partnership, Acquisition and Capacity Strategy
- 16.8 Regional Expansion Priorities
- 16.9 Short-, Medium- and Long-Term Actions
Chapter 17 Competition Outlook
- 17.1 Industry Competition Characteristics
- 17.2 Market Structure and Concentration
- 17.3 Market Share and Competitive Positioning, 2025
- 17.4 Company-Wise Revenue and Product Benchmarking
- 17.5 Production and Service Capacity Benchmarking
- 17.6 Technology, Pricing and Differentiation
- 17.7 Regional Footprint and Distribution Strength
- 17.8 Mergers, Acquisitions and Strategic Alliances
- 17.9 New Entrants and Competitive Threats
- 17.10 Porter's Five Forces and Industry Attractiveness
- 17.11 Competitive Outlook, 2025-2035
Chapter 18 Company Profiles
- 18.1 Company Coverage and Selection Criteria
- 18.2 Accenture / CyberCX
- 18.2.1 Business Description
- 18.2.2 Company Ownership and Geographic Presence
- 18.2.3 Product and Service Portfolio
- 18.2.4 Manufacturing and Operating Footprint
- 18.2.5 Financial Performance and Investment
- 18.2.6 Market Share and Competitive Position
- 18.2.7 Technology and Innovation Capabilities
- 18.2.8 Strategic Alliances or Partnerships
- 18.2.9 Recent Developments
- 18.2.10 Growth Strategy and Outlook
- 18.3 CrowdStrike
- 18.4 Palo Alto Networks
- 18.5 Fortinet
- 18.6 Microsoft
- 18.7 Other Relevant Market Participants
Note: Every listed company is profiled on the structure shown under the first company. The company list is preliminary and may change based on research findings, market developments, data availability and client requirements.
Chapter 19 Disclaimer
- 19.1 Research and Forecast Disclaimer
- 19.2 Data Source and Estimation Limitations
Note: The depth of individual sections depends on data availability for this market. Volume, capacity, trade and other unit-based metrics are included where applicable.

