
| REPORT ATTRIBUTE | DETAILS |
|---|---|
| Historical Period | 2019-2022 |
| Base Year | 2023 |
| Forecast Period | 2024-2032 |
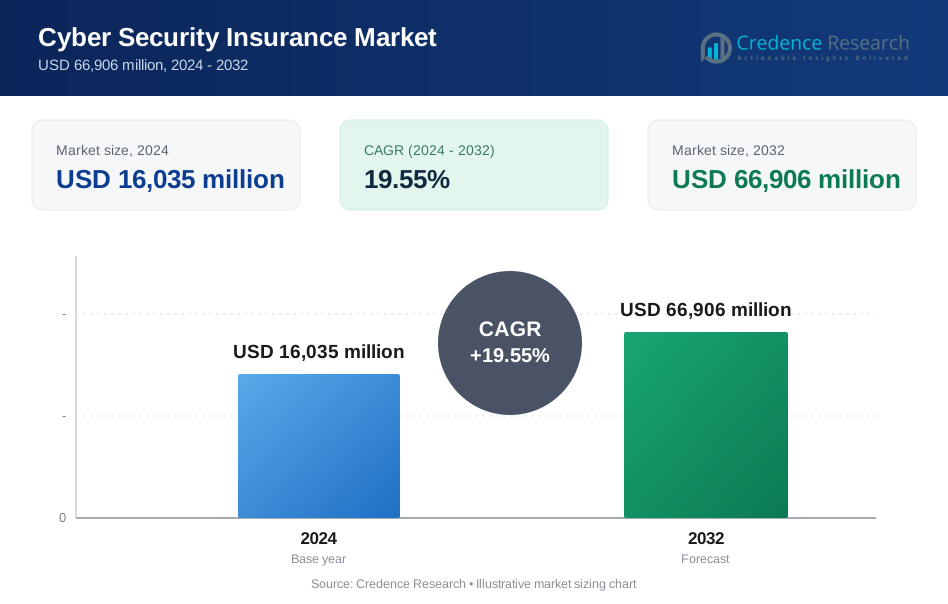
| Cyber Security Insurance Market Size 2024 | USD 16,035 Million |
| Cyber Security Insurance Market, CAGR | 19.55% |
| Cyber Security Insurance Market Size 2032 | USD 66,906 Million |
Market Overview
The Cyber Security Insurance Market is projected to grow from USD 16,035 million in 2024 to USD 66,906 million by 2032, reflecting a robust compound annual growth rate (CAGR) of 19.55%.
The Cyber Security Insurance Market is driven by the increasing frequency of cyberattacks and data breaches, prompting businesses to seek protection against financial losses and liabilities. Growing regulatory requirements, such as GDPR and CCPA, further push companies to invest in cyber insurance. Additionally, the rise in digital transformation across industries increases the risk exposure, fueling demand for comprehensive coverage. Key market trends include the adoption of AI-driven risk assessment tools and the development of customizable insurance policies tailored to specific business needs, reflecting the evolving landscape of cybersecurity threats and insurance solutions.
The cybersecurity insurance market shows strong regional growth, with North America leading due to the prevalence of cyber threats and stringent regulations. The US dominates this region, driven by a high adoption rate of cybersecurity insurance among businesses. In Europe, the GDPR has significantly boosted demand for cyber insurance, while Asia-Pacific is seeing rapid growth due to increasing digitalization and cyber risk awareness. Key players driving the market include BitSight, Microsoft, and Check Point from the US, alongside Allianz (Germany), Aon (UK), and Beazley (UK), offering comprehensive solutions and insurance products tailored to specific industry needs.
Market Drivers
Stricter Regulatory Compliance
Stricter regulatory frameworks are another key driver in the cyber security insurance market. Governments around the world, including the United States, the European Union, and India, have introduced stringent data protection laws, such as GDPR and CCPA. For instance, these regulations impose hefty fines and penalties on companies that fail to adequately safeguard personal data, further incentivizing businesses to invest in cyber insurance. These regulations impose hefty fines and penalties on companies that fail to adequately safeguard personal data, further incentivizing businesses to invest in cyber insurance. Additionally, industry-specific regulations in sectors like healthcare, finance, and energy create further compliance challenges, pushing companies to seek insurance as a means to ensure protection and adherence to these mandates.
Financial Impact of Cyber Incidents
Cyber incidents can lead to severe financial repercussions, both direct and indirect, which has increased demand for cyber security insurance. For instance, direct costs include lost revenue, legal fees, and regulatory fines, which can quickly accumulate, especially after major breaches. Indirect costs, such as damage to a company’s reputation, loss of customer trust, and the disruption of business operations, can be even more significant in the long term. These financial impacts often push organizations to prioritize securing insurance coverage to safeguard against unforeseen cyber-related expenses.
Increasing Frequency and Sophistication of Cyber Threats
The rising prevalence of cyber threats, such as ransomware attacks, data breaches, and phishing scams, is significantly driving the demand for cyber security insurance. Ransomware attacks, which have notably targeted critical infrastructure and businesses, have surged, leading to devastating financial and operational consequences. Similarly, data breaches, which expose sensitive information like personal details and intellectual property, remain a major concern for companies across all sectors. Phishing attacks and social engineering techniques are also becoming increasingly sophisticated, making it easier for cybercriminals to gain unauthorized access to corporate systems. These evolving threats push organizations to seek comprehensive insurance coverage to mitigate risks and recover from potential losses.
Digital Transformation and Risk Preparedness
As businesses increasingly undergo digital transformation and adopt cloud computing, their exposure to cyber risks grows. The integration of advanced technologies has introduced new security challenges, making companies more vulnerable to attacks. At the same time, heightened risk awareness has led organizations to take proactive steps in improving their cybersecurity measures. Businesses are focusing on bolstering their defenses and managing risks, which often results in more favorable insurance premiums. Additionally, the shortage of skilled cybersecurity professionals further underscores the need for outsourcing security functions and purchasing cyber insurance as a safeguard.
Market Trends
Expanded Coverage Options and Risk-Based Pricing
The cyber security insurance market is evolving with a greater focus on specialized coverage and risk-based pricing. Insurers are developing policies tailored to meet the specific needs of various industries, offering more comprehensive options that address a wide range of cyber risks. These expanded policies now cover threats such as data breaches, ransomware attacks, and business interruptions, providing businesses with the security they need in an increasingly digital landscape. For instance, a survey conducted that the number of ransomware attacks surged significantly in 2023, prompting insurers to expand their coverage options. The growing complexity of cyber threats has pushed insurers to offer policies that go beyond basic coverage, allowing businesses to customize their insurance to their unique operational risks. Alongside these expanded options, insurers are implementing risk-based pricing strategies that leverage data analytics to assess each organization’s cyber risk profile. Companies with stronger cybersecurity defenses and proactive risk management strategies can benefit from preferred rates or discounts. This shift toward data-driven underwriting incentivizes organizations to strengthen their cybersecurity posture, not only reducing their exposure to threats but also potentially lowering insurance premiums. The combination of expanded coverage and personalized pricing models reflects the growing sophistication of both cyber threats and the insurance industry’s response.
Integration of Cyber Threat Intelligence and Consulting Services
Insurers are increasingly integrating cyber threat intelligence into their service offerings, providing real-time data on emerging risks. By leveraging threat intelligence, insurers can adjust their coverage based on the evolving landscape of cyber threats, ensuring that clients are protected against new and emerging risks. This proactive approach also allows insurers to offer value-added services, such as cybersecurity consulting, to help businesses strengthen their defenses. These consulting services, often included as part of comprehensive insurance packages, provide organizations with the tools and insights they need to identify vulnerabilities and mitigate risks. The integration of threat intelligence and consulting services represents a shift from reactive to proactive risk management, allowing businesses to stay ahead of potential cyber threats. Moreover, insurers are increasingly collaborating with governments through public-private partnerships to enhance cyber awareness and strengthen the overall resilience of the digital ecosystem. These partnerships promote a shared responsibility for cyber risk management, combining the resources and expertise of both private and public sectors to address the challenges posed by a rapidly evolving cyber landscape. Additionally, advancements in technology, such as artificial intelligence and blockchain, are being utilized to detect threats and secure data more effectively, further enhancing the capabilities of both insurers and their clients.
Market Challenges Analysis
Underwriting and Claims Complexity
The dynamic nature of the cyber threat landscape poses significant challenges for underwriting in the cyber security insurance market. With cyber threats constantly evolving, insurers struggle to accurately assess risk and price policies accordingly. For instance, a report by the National Association of Insurance Commissioners (NAIC) highlights that insurers face difficulties in obtaining sufficient data to model cyber risks effectively. This unpredictability is compounded by data limitations, as insurers often lack the comprehensive datasets needed to predict future losses with accuracy, increasing the potential for pricing errors. The complexity doesn't stop at underwriting; claims processing is equally intricate. Insurers face difficulties in determining whether a cyber incident was directly caused by a covered peril, which can complicate claim approvals. Moreover, quantifying losses, particularly intangible damages like reputational harm or loss of customer trust, proves challenging. These complexities make it harder for insurers to develop accurate pricing models and payout mechanisms, leaving room for disputes during claims processing. As the landscape of cyber threats continues to evolve, insurers must find ways to improve their risk assessment and claims adjudication processes to stay competitive and effective.
Moral Hazard and Regulatory Uncertainty
Moral hazard is another significant challenge in the cyber security insurance market. Some organizations may become complacent in their cybersecurity practices, relying too heavily on their insurance policies to cover any potential losses. This complacency increases the risk of preventable breaches and amplifies potential losses. In addition, there is the risk of fraudulent claims, where organizations may exaggerate or fabricate cyber incidents to obtain insurance payouts, adding another layer of complexity to the claims process. Regulatory uncertainty further complicates the landscape for insurers. Cybersecurity regulations are constantly evolving, and insurers must stay compliant with these changing laws. For those operating across multiple jurisdictions, international compliance becomes a significant hurdle, as navigating the patchwork of laws can be both complex and costly. Insurers must continuously adapt to new regulatory frameworks while ensuring that their policies remain viable and compliant across borders. This regulatory uncertainty adds to the already complex environment, requiring insurers to be both flexible and vigilant in their operations.
Market Segmentation Analysis:
By Offering:
The cybersecurity insurance market is divided into solutions and services segments, each playing a critical role in addressing diverse cyber risks. The solution segment includes specialized tools like cybersecurity insurance analytics platforms, disaster recovery, and business continuity solutions. It also encompasses various cybersecurity solutions, such as cyber risk and vulnerability assessments and cybersecurity resilience services, which help organizations detect, manage, and mitigate cyber threats effectively. The services segment provides consulting or advisory support, security awareness training, and infrastructure services, such as implementation, support, and maintenance. These offerings enable companies to strengthen their cybersecurity infrastructure and prepare for potential cyber incidents, ensuring comprehensive risk management.
By Insurance Coverage:
Cybersecurity insurance policies provide varying degrees of coverage based on specific risks, with two main categories being data breach and cyber liability insurance. Data breach coverage includes protection against data loss, denial of service, ransomware attacks, and other risks like third-party data exposure, business disruption, and social engineering. Cyber liability insurance is further categorized by type and source. Coverage includes protection against data protection and privacy costs, non-compliance penalties, and intellectual property risks. It targets both internal and external threats, covering risks caused by human error, system failures, and inadequate IT security measures, ensuring businesses are shielded from the financial repercussions of cyber incidents.
Segments:
Based on Offering:
- Solution
- Cybersecurity insurance analytics platform
- Disaster recovery and business continuity
- Cybersecurity solution
- Cyber risk and vulnerability assessment
- Cybersecurity resilience
- Service
- Consulting/ Advisory
- Security awareness training
- Others (infrastructure services, implementation, and support and maintenance)
Based on Insurance Coverage:
- Data breach
- Data loss
- Denial of service and down-time
- Ransomware attacks
- Others (third party data, business disruption, and social engineering)
- Cyber liability
- Type
- Data protection and privacy costs
- Non-compliance penalty
- Brand and related intellectual property protection
- Others (human error, systems failure, controls framework, Inadequate IT security measures, and non-security related IT)
- Source/ Target
- Internal
- External
- Type
Based on Compliance Requirements:
- Healthcare Compliance
- Financial Services Compliance
- GDPR Compliance
- Data Privacy Compliance
- Other Compliances
Based on the Insurance type:
- Packaged
- Stand-alone
Based on the End user:
- Technology provider
- Insurance companies
- Third-party administrators, brokers, and consultancies
- Government agencies
- Insurance provider
- Financial services
- IT and ITES
- Healthcare and life science
- Retail and ecommerce
- Telecom
- Travel, tourism, and hospitality
- Others (Education, Manufacturing, Energy and Utilities, and Government)
Based on the Geography:
- North America
- U.S.
- Canada
- Mexico
- Europe
- Germany
- France
- U.K.
- Italy
- Spain
- Rest of Europe
- Asia Pacific
- China
- Japan
- India
- South Korea
- South-east Asia
- Rest of Asia Pacific
- Latin America
- Brazil
- Argentina
- Rest of Latin America
- Middle East & Africa
- GCC Countries
- South Africa
- Rest of the Middle East and Africa
Regional Analysis
North America
North America holds the largest market share in the global cybersecurity insurance market, accounting for over 35%. The region's dominance is driven by the high incidence of cyberattacks and the presence of stringent data protection regulations, such as the California Consumer Privacy Act (CCPA) and the Health Insurance Portability and Accountability Act (HIPAA). These regulations compel businesses to adopt robust cybersecurity measures, including insurance coverage to mitigate financial risks. Additionally, the region's mature insurance industry and advanced cybersecurity infrastructure contribute to the strong demand for cyber insurance. Key sectors like healthcare, finance, and retail are especially vulnerable to data breaches and ransomware attacks, further propelling market growth in North America.
Europe
Europe is the second-largest market, with a significant share of around 25%. The implementation of the General Data Protection Regulation (GDPR) has been a major driver of cybersecurity insurance adoption in the region. GDPR imposes strict penalties for data breaches, encouraging organizations to invest in cyber insurance as part of their risk management strategy. The region has also seen a rise in cyberattacks, particularly ransomware incidents targeting critical infrastructure and businesses. Countries like the UK, Germany, and France are at the forefront of the market due to their developed insurance sectors and heightened focus on cybersecurity. The growing adoption of digital technologies and cloud computing in Europe further emphasizes the need for comprehensive cybersecurity insurance.
Key Player Analysis
- BitSight (US)
- Prevalent (US)
- RedSeal (US)
- SecurityScorecard (US)
- Cyber Indemnity Solutions (Australia)
- Cisco (US)
- UpGuard (US)
- Microsoft (US)
- Check Point (US)
- AttackIQ (US)
- SentinelOne (US)
- Broadcom (US)
- Accenture (Ireland)
- Cylance (US)
- Trellix (US)
- CyberArk (US)
- CYE (Israel)
- SecurIT360 (US)
- Founder Shield (US)
- Allianz (Germany)
- AIG (US)
- Aon (UK)
- Arthur J. Gallagher & Co (US)
- Travelers Insurance (US)
- AXA XL (US)
- AXIS Capital (Bermuda)
- Beazley (UK)
- Chubb (Switzerland)
- CNA Financial (US)
- Fairfax Financial (Canada)
- Liberty Mutual (US)
- Lloyd’s of London (UK)
- Lockton (US)
- Munich Re Group (Germany)
- Sompo International (Bermuda)
- At-Bay (US)
- Cybernance (US)
- Coalition (US)
- Resilience (US)
- Kovrr (Israel)
- Sayata Labs (Israel)
- Zeguro (US)
- Ivanti (US)
- SafeBreach (US)
- Cronus Cyber Technologies (Israel)
Competitive Analysis
The cybersecurity insurance market is highly competitive, with key players such as BitSight, Microsoft, Cisco, Check Point, Allianz, AIG, Aon, UpGuard, AXA XL, Beazley, and Chubb dominating the landscape. These companies differentiate themselves by offering comprehensive solutions that integrate cyber risk assessment tools, consulting services, and customized insurance coverage for businesses across various sectors. The competitive edge lies in their ability to provide proactive risk management services, such as cybersecurity awareness training and real-time threat intelligence. These market leaders are constantly innovating and expanding their portfolios to address the evolving cyber threat landscape and meet stringent regulatory requirements globally.
Recent Developments
- In July 2024, BitSight announced the 2024 Ratings Algorithm Update (RAU), which changes the lifetime of Patching Cadence findings from 300 days to 90 days.
- In February 2024, SecurityScorecard announced significant momentum coming into 2024, driven by strong new customer acquisition and the launch of solutions in adjacent markets, including threat intelligence and external attack surface management.
- In June 2024, Cisco announced new AI-powered innovations and investments at Cisco Live 2024, including a $1 Billion Global AI Investment Fund to advance industry innovation and customer readiness.
- In May 2024, Microsoft announced new features at Microsoft Build 2024, including updates to its AI chatbot Copilot and new Microsoft Teams tools.
Market Concentration & Characteristics
The cybersecurity insurance market exhibits moderate concentration, with a mix of established players and emerging startups. Major insurers like UpGuard, Allianz, AIG, and Munich Re Group, AXA XL hold significant market shares, benefiting from their extensive resources and expertise in risk assessment. However, the presence of innovative startups such as Coalition and At-Bay injects dynamism into the market, offering tailored solutions that cater to niche segments. The industry is characterized by rapid technological advancements, as insurers increasingly leverage data analytics and artificial intelligence to enhance underwriting processes and pricing models. Additionally, there is a growing emphasis on providing value-added services, such as cybersecurity consulting and incident response planning, to differentiate offerings. This competitive landscape encourages collaboration between insurance companies and cybersecurity firms, fostering a holistic approach to risk management. Overall, the market's characteristics reflect a balance between established practices and the need for innovation in response to evolving cyber threats.
Report Coverage
The research report offers an in-depth analysis based on Offering, Insurance Coverage, Compliance Requirements, Insurance type, End user and Geography. It details leading market players, providing an overview of their business, product offerings, investments, revenue streams, and key applications. Additionally, the report includes insights into the competitive environment, SWOT analysis, current market trends, as well as the primary drivers and constraints. Furthermore, it discusses various factors that have driven market expansion in recent years. The report also explores market dynamics, regulatory scenarios, and technological advancements that are shaping the industry. It assesses the impact of external factors and global economic changes on market growth. Lastly, it provides strategic recommendations for new entrants and established companies to navigate the complexities of the market.
Future Outlook
- The demand for comprehensive cyber insurance coverage will continue to rise as cyber threats become more sophisticated and prevalent.
- Insurers will increasingly leverage advanced data analytics and machine learning to enhance risk assessment and pricing strategies.
- Regulatory compliance will drive organizations to seek more robust insurance solutions that address evolving legal requirements.
- Cybersecurity consulting services will become a standard offering alongside insurance policies to support businesses in risk mitigation.
- The integration of threat intelligence into insurance products will help companies proactively manage and respond to cyber risks.
- Collaboration between insurance providers and cybersecurity firms will increase to offer holistic solutions that encompass prevention and recovery.
- Emerging technologies, such as blockchain, will play a role in enhancing the transparency and security of insurance transactions.
- Small and medium-sized enterprises will increasingly prioritize cyber insurance as awareness of cyber risks grows.
- Global expansion of cyber insurance products will address cross-border risks faced by multinational companies.
- The industry will adapt to new threats, such as AI-driven attacks, necessitating ongoing innovation in insurance offerings.
Request a Free Sample
Fill in your details and we'll send you a free sample report.
- Sample data tables & charts
- Research methodology
Need a Custom Version of This Report?
Tailor the scope, geography, or segments to your exact requirements.
- Custom geography or segment scope
- Direct access to our analyst team
Frequently Asked Questions
What is the current size of the Cyber Security Insurance Market?
What factors are driving the growth of the Cyber Security Insurance Market?
What are the key segments within the Cyber Security Insurance Market?
What are some challenges faced by the Cyber Security Insurance Market?
Who are the major players in the Cyber Security Insurance Market?
Table of Content
Chapter 1. Report Introduction
- 1.1 Report Description & Purpose
- 1.1.1 Report Title & Market Definition
- 1.1.2 Unique Selling Propositions (USP) & Key Differentiators
- 1.1.3 Value Proposition for Stakeholders
- 1.2 Research Objectives
- 1.2.1 Market Sizing Objectives (Volume & Revenue)
- 1.2.2 Segmentation Objectives
- 1.2.3 Competitive Intelligence Objectives
- 1.2.4 Forecast & Scenario Objectives
- 1.3 Report Scope
- 1.3.1 Cyber Security Insurance Scope – Types & Subtypes Covered
- 1.3.2 Geographic Scope – Regions & Countries Covered
- 1.3.3 Historical Period, Base Year & Forecast Period (2024; forecast to 2032)
- 1.3.4 Inclusions & Exclusions
- 1.4 HS Code & Classification Framework
- 1.5 Currency, Units & Pricing Basis
- 1.6 Target Stakeholders
- 1.7 Limitations & Assumptions
Chapter 2. Executive Summary
- 2.1 Global Cyber Security Insurance Market Snapshot
- 2.1.1 Market Size – Historical (2024) & Forecast (2024-2032) (2024: USD 16,035 million → 2032: USD 66,906 million)
- 2.1.2 Volume & Revenue – Global Totals
- 2.1.3 Key Market Highlights – Top Five Facts
- 2.2 Cyber Security Insurance Market Segmentation Snapshot
- 2.2.1 Market Split by Region – 2024 vs. 2032
- 2.3 Competitive Snapshot
- 2.3.1 Top 10 Players by Revenue Share – 2024
- 2.3.2 Top 10 Players by Volume Share – 2024
- 2.3.3 Recent Strategic Developments (18-Month Summary)
- 2.4 Key Investment Highlights & Strategic Conclusions
Chapter 3. Cyber Security Insurance Market Dynamics & Industry Analysis
- 3.1 Market Overview & Context
- 3.1.1 Cyber Security Insurance Market Position in the Broader Automotive Value Chain
- 3.1.2 OEM vs. Replacement Market Dynamics
- 3.1.3 Market Maturity & Development Stage by Region
- 3.2 Cyber Security Insurance Market Drivers
- 3.3 Cyber Security Insurance Market Restraints & Challenges
- 3.4 Cyber Security Insurance Market Opportunities
- 3.5 Porter's Five Forces Analysis
- 3.5.1 Threat of New Entrants
- 3.5.2 Bargaining Power of Suppliers
- 3.5.3 Bargaining Power of Buyers
- 3.5.4 Threat of Substitutes
- 3.5.5 Competitive Rivalry – Intensity Assessment
- 3.6 Cyber Security Insurance Value Chain Analysis
- 3.6.1 Upstream – Raw Material/Input Suppliers
- 3.6.1.1 Raw Material/Input 1
- 3.6.1.2 Raw Material/Input 2
- 3.6.1.3 Raw Material/Input 3
- 3.6.2 Midstream – Production/Manufacturing/Service Delivery
- 3.6.2.1 Production/Process Overview
- 3.6.2.2 Key Facility Locations & Capacity by Manufacturer
- 3.6.3 Downstream – Distribution & End Consumer
- 3.6.3.1 Primary Channel – B2B/OEM
- 3.6.3.2 Secondary Channels – Dealer, Retail, Online, Direct
- 3.6.4 Value Chain Profitability Analysis
- 3.6.1 Upstream – Raw Material/Input Suppliers
- 3.7 PESTEL Analysis
- 3.7.1 Political Factors
- 3.7.2 Economic Factors
- 3.7.3 Social Factors
- 3.7.4 Technological Factors
- 3.7.5 Environmental Factors
- 3.7.6 Legal Factors
- 3.8 Cyber Security Insurance Supply Chain Analysis
- 3.8.1 Raw Material/Input Supply Risk Assessment
- 3.8.2 Manufacturing Concentration Risk (Geographic Exposure)
- 3.8.3 Trade Disruption Impact Analysis
- 3.9 Regulatory & Policy Landscape
Note: The regulatory and policy landscape section covers regulations based on their applicability to the market, Cyber Security Insurance category, geography, and scope of the study. Only regulatory frameworks with a material impact on operations, compliance, trade, sustainability, or market access are analyzed in detail.
Chapter 4. Key Investment Pockets & Opportunity Analysis
- 4.1 Cyber Security Insurance Market Attractiveness Analysis
- 4.1.1 By Region – Investment Attractiveness Matrix (Volume × CAGR)
- 4.2 Absolute Revenue Growth Opportunity
- 4.2.1 By Region – Absolute USD Growth Through 2032
- 4.3 Incremental Volume Opportunity
- 4.3.1 By Region – Incremental Volume Through 2032
- 4.3.2 Segment – Incremental Volume
- 4.4 Emerging Submarket Opportunity Deep Dive (Subject to Applicability)
- 4.5 Emerging Market Opportunity Scorecards
- 4.5.1 United States
- 4.5.2 Europe
- 4.5.3 Asia
- 4.5.4 Middle East & Africa
Note: Emerging Market Opportunity Scorecards will be included based on relevance and strategic importance. Regions listed are indicative and may vary depending on data availability and market dynamics.
Chapter 5. Cyber Security Insurance Import-Export Analysis & Trade Flows
- 5.1 Global Trade Overview
- 5.1.1 Global Export Value by Country (2024)
- 5.1.2 Global Export Volume by Country (2024)
- 5.1.3 Global Import Value by Country (2024)
- 5.1.4 Global Import Volume by Country (2024)
- 5.1.5 Net Trade Balance by Country (2024)
- 5.2 Export Analysis – Segment
- 5.2.1 Type 1 (HS Code)
- 5.2.2 Type 2 (HS Code)
- 5.2.3 Type 3 (HS Code)
- 5.2.4 Type 4 (HS Code)
- 5.2.5 Type 5 (HS Code)
- 5.3 Import Analysis – Segment
- 5.3.1 Type 1 (HS Code)
- 5.3.2 Type 2 (HS Code)
- 5.3.3 Type 3 (HS Code)
- 5.3.4 Type 4 (HS Code)
- 5.3.5 Type 5 (HS Code)
- 5.4 Average Unit Trade Prices
- 5.4.1 Average Export Price – Segment & Country
- 5.4.2 Average Import Price – Segment & Source Country
- 5.4.3 Price Trends (2024)
- 5.5 Key Trade Route Analysis
- 5.5.1 Trade Route 1
- 5.5.2 Trade Route 2
- 5.5.3 Trade Route 3
- 5.5.4 Trade Route 4
- 5.5.5 Trade Route 5
- 5.6 Trade Policy Impact Assessment
- 5.6.1 US Anti-Dumping & Section 301 Tariffs
- 5.6.2 EU Customs Union Impact
- 5.6.3 Major Free Trade Agreements
- 5.6.4 USMCA Rules of Origin
Note: Trade policy analysis will be included only where relevant to the Cyber Security Insurance market.
Chapter 6. Competitive Landscape & Company Benchmarking
- 6.1 Cyber Security Insurance Market Concentration & Structure
- 6.1.1 Herfindahl-Hirschman Index (HHI) – vs. 2024
- 6.1.2 Tier 1, Tier 2 & Tier 3 Market Structure
- 6.1.3 Global, Regional & Local Player Dynamics
- 6.2 Cyber Security Insurance Market Share Analysis – 2024
- 6.2.1 Global Revenue Share by Company
- 6.2.2 Global Volume Share by Company
- 6.2.3 Regional Revenue Share
- 6.2.4 Market Share Evolution ( vs. 2024)
- 6.2.5 OEM Segment Share by Company
- 6.2.6 Replacement Segment Share by Company
- 6.3 Production/Delivery Capacity & Facility Analysis
- 6.3.1 Global Installed Capacity
- 6.3.2 Capacity Utilization Rates
- 6.3.3 Production/Output Volume
- 6.3.4 Facility Locations & Capacity Map
- 6.3.5 Planned Capacity Additions
- 6.4 Cyber Security Insurance Competitive Benchmarking Matrix
- 6.4.1 Revenue, Volume, CAGR & Profitability Comparison
- 6.4.2 Channel Revenue Mix
- 6.4.3 Geographic Revenue Exposure
- 6.4.4 R&D Intensity
- 6.4.5 Sustainability Maturity
- 6.5 Strategic Developments in Cyber Security Insurance (Last 24 Months)
- 6.5.1 Mergers, Acquisitions & Divestments
- 6.5.2 New Cyber Security Insurance Launches
- 6.5.3 Facility Expansions
- 6.5.4 Strategic Alliances, Joint Ventures & Partnerships
- 6.5.5 Distribution Expansion & Market Entry
- 6.5.6 Sustainability & ESG Initiatives
- 6.6 Competitive Strategy Mapping
- 6.6.1 Leader, Challenger, Follower & Niche Classification
- 6.6.2 Pricing Strategy Comparison
- 6.6.3 Channel Strategy Matrix
Note: Strategic developments are included based on their materiality and the availability of reliable information.
Chapter 7. Global Cyber Security Insurance Market – By Distribution Channel
- 7.1 Segment Overview
- 7.1.1 Volume & Revenue Split by Channel (2024 & 2032)
- 7.1.2 Channel Mix Evolution (2024-2032)
Chapter 8. Regional Market Analysis – Global Overview
- 8.1 Global Regional Overview
- 8.1.1 Regional Volume Share
- 8.1.2 Regional Revenue Share
- 8.1.3 Regional Volume by Region
- 8.1.4 Regional Revenue by Region
- 8.1.5 Regional Forecast Through 2032
- 8.2 Cross-Regional Segment Analysis
- 8.2.1 By Distribution Channel
- 8.2.2 By Brand/Price Tier
Chapter 9. North America Cyber Security Insurance Market
- 9.1 United States
- 9.2 Canada
- 9.3 Mexico
Chapter 10. Europe Cyber Security Insurance Market
- 10.1 Germany
- 10.2 France
- 10.3 Italy
- 10.4 United Kingdom
- 10.5 Spain
- 10.6 Poland
- 10.7 Russia
- 10.8 Netherlands
- 10.9 Belgium
- 10.10 Sweden
- 10.11 Denmark
- 10.12 Norway
- 10.13 Rest of Europe
Chapter 11. Asia Pacific Cyber Security Insurance Market
- 11.1 China
- 11.2 India
- 11.3 Japan
- 11.4 South Korea
- 11.5 Thailand
- 11.6 Indonesia
- 11.7 Vietnam
- 11.8 Malaysia
- 11.9 Australia
- 11.10 Rest of Asia Pacific
Chapter 12. Latin America Cyber Security Insurance Market
- 12.1 Brazil
- 12.2 Argentina
- 12.3 Colombia
- 12.4 Chile
- 12.5 Rest of Latin America
Chapter 13. Middle East Cyber Security Insurance Market
- 13.1 Saudi Arabia
- 13.2 United Arab Emirates
- 13.3 Turkey
- 13.4 Israel
- 13.5 Iran
- 13.6 Rest of the Middle East
Chapter 14. Africa Cyber Security Insurance Market
- 14.1 South Africa
- 14.2 Egypt
- 14.3 Nigeria
- 14.4 Morocco
- 14.5 Rest of Africa
Chapter 15. Cyber Security Insurance Company Profiles
- 15.1 [Company 01]
- 15.1.1 Company Overview
- 15.1.2 Key Management Personnel
- 15.1.3 Products & Services Portfolio
- 15.1.4 Financial Performance
- 15.1.5 Key Market Focus & Geographic Presence
- 15.1.6 Recent Developments & Strategic Initiatives
Note: The company profile list is preliminary and may change based on research findings, market developments, data availability, and client requirements.
Chapter 16. Appendices
- Appendix A – List of Abbreviations & Acronyms
- Appendix B – Industry Classification Code Reference – Full Series
- Appendix C – Production & Capacity Data Tables
- Appendix D – End-Use & Demand Base Tables
- Appendix E – Consumption & Replacement Rate Assumptions
- Appendix F – ASP Reference Tables
- Appendix G – Manufacturing & Facility Database
- Appendix H – Import-Export Data Tables
- Appendix I – Regulatory Summary Tables
- Appendix J – Primary Research Participant List (Anonymized)
- Appendix K – Primary Research Questionnaire Framework
- Appendix L – Data Sources & Bibliography
- Appendix M – Market Size Divergence & Source Comparison
Chapter 17. Research Methodology
- 17.1 Research Framework & Philosophy
- 17.2 Secondary Research – Sources, Hierarchy & Data Extraction
- 17.3 Data Modeling – Bottom-Up & Top-Down Market Sizing
- 17.4 Primary Research – Stakeholder Framework, LOI & Sample Sizes
- 17.5 Forecast Methodology – Regression, Scenario & Sensitivity Analysis
- 17.6 Quality Control – Four-Layer Validation Framework
- 17.7 Limitations & Standard Assumptions
- 17.8 Disclaimer
