
| REPORT ATTRIBUTE | DETAILS |
|---|---|
| Historical Period | 2020-2023 |
| Base Year | 2024 |
| Forecast Period | 2025-2032 |
| Cyber Risk Assessment Market Size 2024 | USD 245622 million |
| Cyber Risk Assessment Market, CAGR | 12.7% |
| Cyber Risk Assessment Market Size 2032 | USD 639,232 million |
Market Overview:
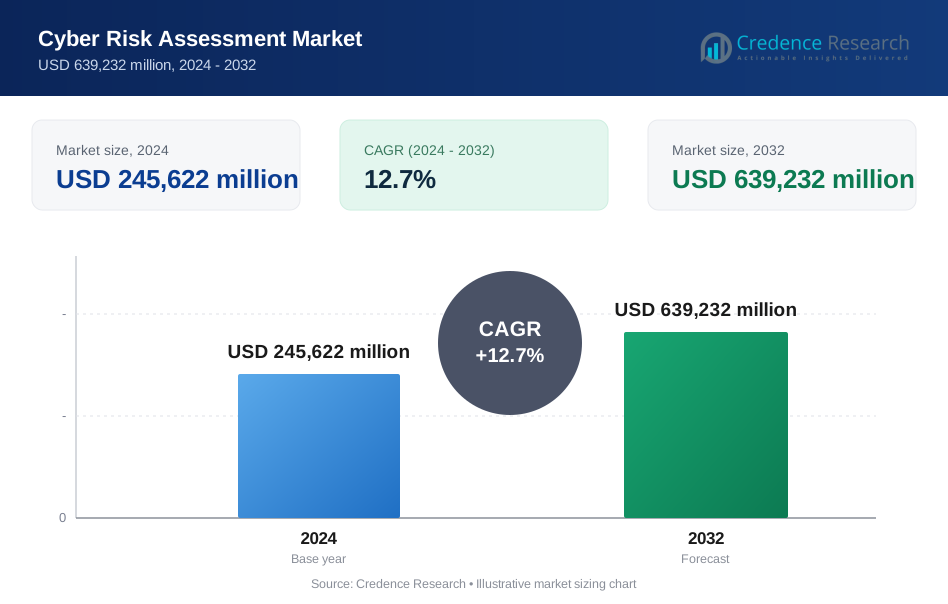
The Cyber Risk Assessment Market is projected to grow from USD 245622 million in 2024 to an estimated USD 639232 million by 2032, with a compound annual growth rate (CAGR) of 12.7% from 2024 to 2032.
Several key factors are propelling the expansion of the cyber risk assessment market. First, the escalating frequency and complexity of cyberattacks, including ransomware, phishing, and advanced persistent threats, have heightened the urgency for robust risk management strategies. For instance, the surge in Iranian cyberattacks on Israeli infrastructure has underscored the vulnerabilities in critical sectors. Second, the rapid adoption of digital transformation initiatives, such as cloud computing and the Internet of Things (IoT), has expanded the attack surface, necessitating advanced risk assessment tools to safeguard digital assets. Third, stringent regulatory requirements and compliance mandates, including the General Data Protection Regulation (GDPR) and the Cybersecurity Maturity Model Certification (CMMC), compel organizations to conduct regular risk assessments to ensure adherence and avoid potential penalties. Additionally, the integration of artificial intelligence (AI) and machine learning (ML) into cybersecurity practices is enhancing the predictive capabilities of risk assessment models, enabling organizations to anticipate and mitigate potential threats more effectively.
Regionally, North America holds a dominant position in the cyber risk assessment market, attributed to the presence of major technology firms, high cybersecurity awareness, and stringent regulatory frameworks. The United States, in particular, has seen increased investments in cybersecurity, with financial institutions allocating significant budgets to bolster their defenses. Europe follows closely, driven by the enforcement of GDPR and other data protection laws that mandate regular risk assessments. The Asia-Pacific region is experiencing the fastest growth, fueled by rapid industrialization, digitalization, and increasing cyber threats targeting emerging economies. Countries like India and China are investing heavily in cybersecurity infrastructure to protect their expanding digital ecosystems. Latin America and the Middle East & Africa regions are also witnessing growth, albeit at a slower pace, as organizations in these areas begin to recognize the importance of cyber risk assessments in the face of rising cyber threats and evolving regulatory landscapes.
Market Insights:
- The Cyber Risk Assessment Market is expected to grow from USD 245,622 million in 2024 to USD 639,232 million by 2032, with a CAGR of 12.7%.
- Rising cyber threats, including ransomware and phishing, are driving businesses to invest in advanced risk management tools to protect their digital assets.
- Digital transformation initiatives such as cloud computing and IoT are expanding the attack surface, increasing the demand for robust cyber risk assessment solutions.
- Stringent regulatory requirements, including GDPR and CMMC, are compelling organizations to adopt regular risk assessments to comply with data protection standards.
- The integration of AI and machine learning technologies is enhancing predictive capabilities and real-time risk assessment, enabling businesses to stay ahead of emerging threats.
- North America dominates the market, driven by high investments in cybersecurity and stringent regulatory frameworks, particularly in the United States.
- The Asia-Pacific region is experiencing rapid growth, with countries like India and China investing heavily in cybersecurity infrastructure to address evolving digital threats.
Market Drivers:
Rising Frequency and Complexity of Cyberattacks
The rapid increase in the frequency and sophistication of cyberattacks is a primary driver for the growth of the Cyber Risk Assessment Market. Cybercriminals are employing increasingly advanced techniques such as ransomware, malware, and phishing to target organizations across various industries. This escalation in cyber threats has prompted businesses to invest heavily in risk assessment tools to identify vulnerabilities in their systems. Organizations recognize that a proactive approach to assessing cyber risks can help them mitigate potential damage and avoid substantial financial and reputational losses. The growing number of high-profile data breaches and security incidents has led to heightened awareness about the importance of continuous risk management strategies.
- For instance, Bitsight, leveraging over 10 years of cyber risk data from millions of entities, has documented a significant rise in ransomware campaigns. Their 2025 report highlights a 25% increase in ransomware attacks and a 53% surge in ransomware group leak sites, reflecting the growing sophistication of cybercriminals targeting mid-sized organizations.
Expanding Digital Transformation and Technological Advancements
The widespread adoption of digital technologies has increased the need for robust cybersecurity frameworks. As businesses embrace cloud computing, Internet of Things (IoT), and other advanced technologies, their digital infrastructure becomes more susceptible to cyber risks. Cyber Risk Assessment Market growth stems from organizations needing to secure a growing array of digital assets and networks. These technologies expand the attack surface, making traditional risk management practices less effective. Assessing and managing these risks is essential for protecting sensitive data and maintaining business continuity. The market responds by offering specialized tools that address the unique challenges posed by modern digital ecosystems.
Stringent Regulatory Requirements and Compliance Mandates
Government regulations and industry standards are playing an influential role in driving demand for cyber risk assessment solutions. Regulations such as the General Data Protection Regulation (GDPR), Health Insurance Portability and Accountability Act (HIPAA), and the Cybersecurity Maturity Model Certification (CMMC) mandate regular assessments to ensure organizations are protecting personal and sensitive information. Non-compliance can result in hefty fines, legal actions, and reputational damage. As regulatory bodies continue to enforce stricter data protection and security measures, companies are compelled to adopt comprehensive risk assessment strategies to ensure adherence to these guidelines. The growing complexity of regulatory environments across industries further contributes to the Cyber Risk Assessment Market's expansion.
- For instance, Wavestone’s benchmark shows that 63% of companies include security clauses in contracts with partners, but only 37% perform regular audits of critical IT suppliers, and just 13% test response and recovery plans with partners on all critical perimeters.
Integration of Artificial Intelligence and Machine Learning in Cyber Risk Assessment
The integration of artificial intelligence (AI) and machine learning (ML) technologies is transforming how businesses approach cyber risk assessments. These technologies enhance the accuracy and efficiency of identifying potential vulnerabilities in real-time. AI and ML algorithms can process vast amounts of data, detecting patterns that may not be visible through traditional risk assessment methods. This enables organizations to proactively identify emerging threats and respond to them more swiftly. Cyber Risk Assessment Market players are increasingly incorporating AI and ML into their solutions to offer more predictive and dynamic tools that improve the overall security posture of organizations. This shift is a key factor in the market's rapid growth, as businesses seek innovative ways to stay ahead of evolving cyber threats.
Market Trends:
Growing Adoption of Automated Cyber Risk Assessment Tools
The Cyber Risk Assessment Market is experiencing a trend toward the increasing adoption of automated risk assessment tools. Businesses are turning to automation to streamline their cybersecurity efforts and reduce the time spent on manual assessments. These automated tools enable organizations to detect vulnerabilities in real-time, improving the speed and efficiency of risk management processes. Automation also allows businesses to conduct continuous assessments, ensuring that their cybersecurity strategies remain up-to-date in the face of emerging threats. As companies seek more scalable solutions, automated tools provide them with the flexibility to handle complex, evolving cyber risks more effectively. The demand for automation is expected to grow as companies prioritize resource efficiency and improved threat detection capabilities.
- For instance, SentinelOne’s Singularity XDR platform achieved 100% prevention and 100% detection rates in the latest MITRE Engenuity ATT&CK evaluations, with the highest analytic coverage (108 out of 109 techniques) and zero detection delays, demonstrating the effectiveness of automation in real-world, high-stakes environments.
Shift Toward Predictive Cyber Risk Assessment Models
Another notable trend in the Cyber Risk Assessment Market is the shift toward predictive models powered by artificial intelligence (AI) and machine learning (ML). Predictive analytics helps organizations move from reactive to proactive risk management, enabling them to anticipate potential cyber threats before they materialize. By analyzing historical data, AI and ML models can predict future vulnerabilities, offering businesses a more comprehensive understanding of their risk landscape. The rise of predictive cyber risk models enhances the ability of organizations to focus on potential risks that could have significant impacts, allowing for a more targeted allocation of resources. This trend is gaining traction as companies strive for greater precision and efficiency in their cybersecurity efforts.
- For instance, CyberSaint’s CyberStrong platform utilizes the world’s largest cyber loss dataset, updated monthly, to provide tailored, predictive risk insights specific to industry, company size, and revenue. The platform supports risk quantification using models such as FAIR and NIST 800-30, translating cyber risk into financial terms and enabling organizations to benchmark their risk posture against industry peers in real time.
Increased Focus on Risk Management for Third-Party Vendors
The growing reliance on third-party vendors and partners is driving a significant trend in the Cyber Risk Assessment Market. Organizations are increasingly recognizing the risks posed by their third-party relationships, especially when it comes to sharing sensitive data and accessing shared networks. Risk assessments now extend beyond internal systems to include the cybersecurity practices of third-party vendors. Companies are seeking solutions that can evaluate the cybersecurity posture of their vendors and ensure that these external partners adhere to the same security standards. This trend highlights the importance of managing the broader supply chain and emphasizes the need for more comprehensive risk management strategies in today’s interconnected business environment.
Integration of Cyber Risk Assessment into Broader Enterprise Risk Management Strategies
The Cyber Risk Assessment Market is also witnessing an integration of cyber risk assessments into broader enterprise risk management (ERM) frameworks. Companies are increasingly aligning their cybersecurity strategies with overall organizational risk management plans. By incorporating cyber risk assessments into ERM, businesses can better understand the interconnectedness of cyber risks with other types of organizational risks, such as financial, operational, and reputational risks. This holistic approach enables organizations to prioritize cybersecurity alongside other critical business concerns, fostering more coordinated and strategic decision-making. As cyber threats continue to evolve, businesses are recognizing the need to embed cyber risk management into their overall risk governance practices.
Market Challenges Analysis:
Difficulty in Keeping Pace with Rapidly Evolving Cyber Threats
One of the primary challenges faced by the Cyber Risk Assessment Market is the difficulty in keeping up with the constantly evolving nature of cyber threats. Cybercriminals are continuously developing new techniques and strategies to breach security systems, making it challenging for businesses to stay ahead of potential risks. Traditional risk assessment tools may struggle to detect new or sophisticated attacks, which leaves organizations vulnerable. The rapid pace of technological advancement in areas like artificial intelligence, machine learning, and cloud computing also increases the complexity of risk management. To effectively mitigate cyber threats, businesses must adopt more dynamic and adaptable assessment methods, but the ever-changing landscape of cybersecurity makes this a significant challenge.
Integration and Resource Constraints for Small to Medium-Sized Enterprises (SMEs)
For many small to medium-sized enterprises (SMEs), the integration of comprehensive cyber risk assessment solutions is a significant challenge. Many SMEs lack the resources, both financial and human, to implement advanced cybersecurity measures or conduct regular risk assessments. The complexity of integrating new technologies into existing infrastructures further complicates the process. As SMEs often have limited in-house expertise, they may find it difficult to interpret the results of risk assessments and apply them effectively. Despite growing awareness of cyber threats, these businesses often struggle to balance cybersecurity with their core operations. Consequently, they may remain exposed to risks due to resource constraints and lack of specialized knowledge in cyber risk management.
Market Opportunities:
Expanding Demand for Risk Assessment in Emerging Markets
The Cyber Risk Assessment Market holds significant opportunities in emerging markets, where rapid digital transformation is driving the adoption of advanced cybersecurity measures. As businesses in regions like Asia-Pacific, Latin America, and the Middle East increasingly adopt digital technologies, the need for robust cyber risk management solutions becomes more pronounced. These regions are witnessing a rise in cybercrime, which has heightened awareness about the importance of proactive risk assessment. Companies in these regions are more inclined to invest in comprehensive cybersecurity frameworks, offering growth potential for market players. The expanding IT infrastructure and government support for cybersecurity initiatives also contribute to the increasing demand for risk assessment tools in these areas.
Integration of Advanced Technologies for Enhanced Risk Assessment
The integration of advanced technologies like artificial intelligence (AI) and machine learning (ML) into the Cyber Risk Assessment Market presents a significant growth opportunity. These technologies allow for predictive risk analysis, helping businesses identify vulnerabilities before they can be exploited. As organizations seek more efficient and accurate risk assessment solutions, the demand for AI-powered tools is expected to rise. Market players can leverage this trend by developing sophisticated, AI-driven platforms that provide real-time, automated assessments. This opens avenues for innovation and greater market penetration, especially for companies offering cutting-edge solutions that integrate seamlessly into existing cybersecurity infrastructures.
Market Segmentation Analysis:
The Cyber Risk Assessment Market is segmented across various dimensions, offering a comprehensive overview of its growth drivers.
By Deployment Mode, the market is divided into On-Premises and Cloud-Based solutions. On-premises solutions provide businesses with more control over their infrastructure and security, while cloud-based solutions offer scalability and flexibility, making them more appealing for organizations with dynamic needs.
- For example, IBM QRadaris a leading on-premises security information and event management (SIEM) platform, deployed by major financial institutions for direct control over sensitive data and infrastructure.
By Service Type segment includes Consulting Services, Managed Services, and Professional Services. Consulting services help organizations understand their cybersecurity needs, while managed services offer ongoing risk management. Professional services cater to specialized project-based requirements, ensuring robust and tailored assessments.
- For example, Secureworks Taegis ManagedXDR provides 24/7 managed detection and response. A manufacturing client reported a 90% reduction in mean time to detect (MTTD) and a 75% reduction in mean time to respond (MTTR) to threats after onboarding ManagedXDR.
By Solution Type includes Vulnerability Assessment, Risk Assessment, Threat Assessment, Penetration Testing Services, and Security Program Assessment. These solutions focus on different aspects of cyber risk, from identifying vulnerabilities to ensuring comprehensive security program effectiveness.
By Security Type segment focuses on Endpoint Security, Network Security, Application Security, and Cloud Security. These categories address specific layers within an organization’s IT infrastructure, offering targeted protection based on the nature of the cyber threats.
By Organization Size includes Small and Medium-sized Enterprises (SMEs) and Large Enterprises. SMEs often require scalable, cost-effective solutions, while large enterprises invest in more complex and comprehensive risk assessments due to their extensive infrastructure.
By End-User Industry segment covers industries such as BFSI, IT and Telecommunications, Government and Defense, Energy, Healthcare, Retail, and more. Each industry faces unique regulatory and cybersecurity challenges, driving demand for specialized solutions.
Segmentation:
By Deployment Mode
- On-Premises
- Cloud-Based
By Service Type
- Consulting Services
- Managed Services
- Professional Services
By Solution Type
- Vulnerability Assessment
- Risk Assessment
- Threat Assessment
- Penetration Testing Services
- Security Program Assessment
- Others (e.g., policy/process assessment, compliance assessment)
By Security Type
- Endpoint Security
- Network Security
- Application Security
- Cloud Security
- Others (e.g., ICS and database security)
By Organization Size
- Small and Medium-sized Enterprises (SMEs)
- Large Enterprises
By End-User Industry
- Banking, Financial Services, and Insurance (BFSI)
- IT and Telecommunications
- Government and Defense
- Energy and Utilities
- Manufacturing
- Healthcare
- Retail
- Others (e.g., media, transport, logistics, education)
By Region
- North America
- U.S.
- Canada
- Mexico
- Europe
- Germany
- France
- U.K.
- Italy
- Spain
- Rest of Europe
- Asia Pacific
- China
- Japan
- India
- South Korea
- South-east Asia
- Rest of Asia Pacific
- Latin America
- Brazil
- Argentina
- Rest of Latin America
- Middle East & Africa
- GCC Countries
- South Africa
- Rest of the Middle East and Africa
Regional Analysis:
North America: Market Leader in Cyber Risk Assessment
North America holds the largest market share in the Cyber Risk Assessment Market, accounting for approximately 40% of the global revenue. The United States, in particular, leads the way due to the presence of major technology firms, a strong regulatory environment, and a high level of cybersecurity awareness. The demand for cyber risk assessment solutions is driven by increasing cyberattacks, stringent regulations like the General Data Protection Regulation (GDPR) and the Cybersecurity Maturity Model Certification (CMMC), and the need for businesses to protect sensitive data. The region’s well-established infrastructure for cybersecurity and high adoption of advanced technologies such as artificial intelligence (AI) and machine learning (ML) further strengthen its position. Organizations in North America are investing heavily in risk management to stay ahead of increasingly sophisticated threats, which contributes to the region's market dominance.
Europe: Strong Regulatory Push and Growing Awareness
Europe holds a significant share in the Cyber Risk Assessment Market, accounting for around 30% of the global market. The region benefits from strict cybersecurity regulations, including GDPR, which require organizations to conduct regular assessments of their cybersecurity risks. European businesses are focusing on strengthening their defenses against cyber threats due to rising concerns about data breaches, financial fraud, and targeted cyberattacks. The growing awareness of cyber risks among European enterprises and government initiatives to enhance cybersecurity are key factors driving market growth. Moreover, countries like the United Kingdom, Germany, and France lead the way in adopting advanced risk assessment solutions, making Europe a key player in the global market.
Asia-Pacific: Rapid Growth Driven by Digital Transformation
The Asia-Pacific (APAC) region is experiencing the fastest growth in the Cyber Risk Assessment Market. This region holds about 20% of the global market share, fueled by rapid digitalization, expanding IT infrastructure, and a growing awareness of cyber threats. Countries like China, India, Japan, and South Korea are witnessing an increasing demand for cybersecurity solutions as businesses embrace cloud computing, the Internet of Things (IoT), and other digital technologies. The rising frequency of cyberattacks targeting businesses in these countries, coupled with government initiatives to bolster cybersecurity, is driving the demand for comprehensive risk assessment solutions. APAC’s expanding economy and technological advancements provide ample opportunities for market players to expand their footprint in the region.
Key Player Analysis:
- Qualysec
- N-iX
- Edvantis
- Dataprise
- ELEKS
- TechMD
- TestArmy
- Astra Security
- Sophos
- Palo Alto Networks
- Rapid7
- Zscaler
- IBM
- Cisco
- CrowdStrike
Competitive Analysis:
The Cyber Risk Assessment Market is highly competitive, with several key players offering comprehensive solutions to address growing cybersecurity threats. Major companies in the market include IBM Corporation, McAfee Corp., Palo Alto Networks, and Rapid7. These companies lead the market by providing advanced risk management tools that utilize artificial intelligence (AI), machine learning (ML), and automation to enhance threat detection and response times. They focus on offering solutions tailored to meet the specific needs of businesses across various industries, such as finance, healthcare, and government. The competitive landscape is also shaped by the increasing adoption of cloud-based risk assessment platforms, which offer scalability and flexibility. Smaller, emerging players are carving a niche by offering specialized, cost-effective solutions targeting specific market segments. As the Cyber Risk Assessment Market continues to grow, innovation in predictive risk analysis and integration with existing cybersecurity frameworks will be key differentiators among competitors.
Recent Developments:
- In April 2025, SentinelOne unveiled the Athena release of its Purple AI platform at the RSA Conference 2025, introducing advanced agentic AI capabilities designed to mirror the deep security reasoning and orchestration of experienced SOC analysts. This new product aims to automate threat detection, triage, and response, helping security teams reduce alert fatigue and accelerate incident remediation across diverse data sources.
- In April 2025, Cyera launched Omni DLP, an AI-native data loss prevention solution that unifies data security tools and leverages intelligence from its recent acquisition of Trail Security. The new product is designed to provide real-time, adaptive data protection across cloud, application, and AI environments, significantly reducing false positives and enabling organizations to focus on credible threats.
- In April 2025, Rockwell Automation introduced its Security Monitoring and Response service, a new offering that delivers continuous, real-time monitoring and rapid threat detection for operational technology (OT) environments. This service, announced at the RSA Conference 2025, is intended to help industrial organizations address rising cyber risks and operational inefficiencies by providing 24/7 expert-led monitoring and response capabilities.
Market Concentration & Characteristics:
The Cyber Risk Assessment Market exhibits a moderate level of concentration, with a few large players holding significant market shares, such as IBM, McAfee, and Palo Alto Networks. These companies dominate the market by offering comprehensive, integrated solutions that cater to a wide range of industries. Smaller, specialized firms also play a vital role by providing niche solutions tailored to specific market needs, such as tools focused on regulatory compliance or cloud-based assessments. The market is characterized by rapid innovation, particularly in areas like AI-driven risk assessment and automation, which enhances the speed and accuracy of threat detection. Companies are increasingly focusing on creating scalable, flexible platforms that integrate seamlessly with existing cybersecurity frameworks. The competitive landscape continues to evolve as new players enter the market and as demand for more advanced and customizable risk management solutions increases.
Report Coverage:
The research report offers an in-depth analysis based on Deployment Mode, Service Type, Solution Type, Security Type, Organization Size and End-User Industry. It details leading market players, providing an overview of their business, product offerings, investments, revenue streams, and key applications. Additionally, the report includes insights into the competitive environment, SWOT analysis, current market trends, as well as the primary drivers and constraints. Furthermore, it discusses various factors that have driven market expansion in recent years. The report also explores market dynamics, regulatory scenarios, and technological advancements that are shaping the industry. It assesses the impact of external factors and global economic changes on market growth. Lastly, it provides strategic recommendations for new entrants and established companies to navigate the complexities of the market.
Future Outlook:
- The Cyber Risk Assessment Market will continue to expand as businesses increasingly prioritize cybersecurity due to rising cyber threats.
- Adoption of AI and machine learning technologies will enhance predictive risk assessment capabilities, allowing faster identification of vulnerabilities.
- Growing regulatory requirements across industries will drive demand for compliance-focused risk assessment solutions.
- Cloud-based risk management tools will gain traction as companies seek scalable, flexible, and cost-effective solutions.
- Increasing digital transformation efforts in emerging markets will contribute to market growth, especially in regions like APAC.
- Automation in risk assessment processes will streamline workflows, reducing human error and improving efficiency.
- Integration of cybersecurity risk assessments into broader enterprise risk management frameworks will become more common.
- Small and medium-sized enterprises (SMEs) will seek more affordable and simplified solutions to manage cyber risks.
- Partnerships and collaborations among cybersecurity firms will enhance solution offerings and market penetration.
- As cyber threats evolve, demand for more specialized risk assessment tools addressing specific industries and threats will rise.
Request a Free Sample
Fill in your details and we'll send you a free sample report.
- Sample data tables & charts
- Research methodology
Market Dynamics
Escalating Frequency and Complexity of Cyberattacks
The increasing sophistication and volume of cyberattacks, such as ransomware and phishing, are compelling organizations to invest in advanced cyber risk assessment tools to proactively identify and mitigate vulnerabilities before they are exploited.
Digital Transformation and Expanding Attack Surface
Widespread adoption of cloud computing, IoT, and other digital technologies is broadening the attack surface, making robust risk assessment solutions essential for safeguarding diverse and distributed digital assets.
Stringent Regulatory Requirements and Compliance Mandates
Regulations like GDPR, HIPAA, and CMMC require organizations to conduct regular cyber risk assessments, driving demand for solutions that help ensure compliance and avoid legal or financial penalties.
Integration of AI and Machine Learning in Risk Assessment
The adoption of AI and ML technologies is enhancing the predictive and real-time capabilities of cyber risk assessment tools, enabling organizations to detect emerging threats faster and respond more effectively.
Growing Focus on Third-Party and Supply Chain Risk
As organizations increasingly rely on third-party vendors and partners, the need to assess and manage external cyber risks is driving demand for comprehensive risk assessment solutions that extend beyond internal systems.
Need a Custom Version of This Report?
Tailor the scope, geography, or segments to your exact requirements.
- Custom geography or segment scope
- Direct access to our analyst team
Frequently Asked Questions
What is the current size of the Cyber Risk Assessment Market?
What factors are driving the growth of the Cyber Risk Assessment Market?
What are some challenges faced by the Cyber Risk Assessment Market?
Who are the major players in the Cyber Risk Assessment Market?
Table of Content
Chapter 1 Market Segmentation
- 1.1 Segmentation Framework
- 1.1.1 Product and Service Classification
- 1.1.2 Application and End-Use Classification
- 1.1.3 Technology and Solution Classification
- 1.1.4 Customer and Distribution Channel Classification
- 1.1.5 Geographic Segmentation
- 1.1.6 Market Segment Definitions and Boundaries
- 1.2 By Service Type
- 1.2.1 Consulting Services
- 1.2.2 Managed Services
- 1.2.3 Professional Services
- 1.3 By Solution Type
- 1.3.1 Vulnerability Assessment
- 1.3.2 Risk Assessment
- 1.3.3 Threat Assessment
- 1.3.4 Penetration Testing Services
- 1.3.5 Security Program Assessment
- 1.4 By Deployment Mode
- 1.4.1 On-Premises
- 1.4.2 Cloud-Based
- 1.5 By End-User Industry
- 1.5.1 Banking, Financial Services, and Insurance (BFSI)
- 1.5.2 IT and Telecommunications
- 1.5.3 Government and Defense
- 1.5.4 Healthcare
- 1.5.5 Manufacturing
- 1.5.6 Retail
Chapter 2 Introduction
- 2.1 Report Objectives and Scope
- 2.2 Product Definition and Industry Terminology
- 2.3 Market Inclusions and Exclusions
- 2.4 Research Process
- 2.4.1 Primary Research and Expert Interviews
- 2.4.2 Secondary Research and Source Review
- 2.4.3 Top-Down and Bottom-Up Estimation
- 2.4.4 Data Triangulation and Verification
- 2.5 Market Size Measurement Basis
- 2.5.1 2024: USD 245,622 million → 2032: USD 639,232 million
- 2.6 Historical and Forecast Reference Periods
- 2.6.1 Base Year: 2024
- 2.6.2 Forecast Period: 2024-2032
- 2.7 Research Assumptions and Limitations
Chapter 3 Executive Summary
- 3.1 Market Snapshot and Key Findings
- 3.2 Base-Year Market Size, 2024
- 3.3 Forecast Market Size, 2032
- 3.4 Revenue and Volume Growth Outlook
- 3.5 Key Demand and Supply Indicators
- 3.6 Leading Market Segments
- 3.7 Fastest-Growing Market Opportunities
- 3.8 Regional Performance Highlights
- 3.9 Technology and Industry Transformation
- 3.10 Competitive Landscape Summary
- 3.11 Analyst View and Strategic Implications
Chapter 4 Global Cyber Risk Assessment Market Trends and Developments
- 4.1 Historical Industry Development
- 4.2 Recent Market Trends and Developments
- 4.3 Demand and Customer Behavior Trends
- 4.4 Technology and Product Innovation
- 4.5 Artificial Intelligence, Automation and Digitalization
- 4.6 Local Manufacturing and Supply Chain Realignment
- 4.7 Industry Partnerships, Mergers and Acquisitions
- 4.8 Sustainability and Circular Economy Developments
- 4.9 Government and Private Sector Investment Trends
- 4.10 Emerging Business Models and Commercialization
- 4.11 Industry Developments and Announcements
Chapter 5 Global Cyber Risk Assessment Market Supply and Demand Analysis
- 5.1 Demand Trend and Consumption Analysis
- 5.2 Demand Forecast, 2024-2032
- 5.3 Supply Chain Structure and Procurement Trends
- 5.4 Supply-Demand Gap and Bottlenecks
- 5.5 Import Dependence and Sourcing Structure
- 5.6 Regional Supply and Demand Concentration
Chapter 6 Global Cyber Risk Assessment Market Pricing Analysis
- 6.1 Pricing Structure and Measurement
- 6.2 Historical Pricing Trends
- 6.3 Pricing Outlook, 2024-2032
- 6.4 Pricing by Product and Market Segment
- 6.5 Geographic Pricing Differences
- 6.6 Key Input, Energy, Labor and Logistics Costs
- 6.7 Contract Pricing and Purchasing Models
- 6.8 Pricing Sensitivity and Competitive Positioning
- 6.9 Price, Margin and Profitability Implications
Chapter 7 Global Cyber Risk Assessment Market Dynamics
- 7.1 Market Growth Drivers
- 7.1.1 Demand-Side Drivers
- 7.1.2 Technology and Innovation Drivers
- 7.1.3 Infrastructure and Investment Drivers
- 7.1.4 Regulatory and Policy Drivers
- 7.2 Market Restraints
- 7.2.1 Cost and Affordability Constraints
- 7.2.2 Technology and Adoption Barriers
- 7.2.3 Supply Chain and Operational Constraints
- 7.3 Market Challenges
- 7.3.1 Competitive Pressure and Margin Erosion
- 7.3.2 Skills, Infrastructure and Implementation Gaps
- 7.4 Emerging Market Opportunities
- 7.5 Market Dynamics Impact and Time-Horizon Assessment
Chapter 8 Global Cyber Risk Assessment Value Chain Analysis
- 8.1 Industry Value Chain Overview
- 8.2 Upstream Suppliers and Critical Inputs
- 8.3 Technology and Component Providers
- 8.4 Manufacturing or Service Delivery
- 8.5 Distribution, Channel Partners and Integrators
- 8.6 Downstream Applications and End Users
- 8.7 Value Addition and Profit Pools
- 8.8 Vertical Integration and Outsourcing
- 8.9 Supplier Concentration and Risk
- 8.10 Supply Chain Localization and Resilience
Chapter 9 Global Cyber Risk Assessment Market Regulations and Policies
- 9.1 Relevant Laws, Standards and Compliance Frameworks
- 9.2 Product, Service, Safety and Quality Requirements
- 9.3 Government Policies, Incentives and Subsidies
- 9.4 Imports, Exports and Trade Barriers
- 9.5 Public Procurement and Local Content Requirements
- 9.6 Data Protection, AI and Cybersecurity Compliance
- 9.7 Upcoming Policy Changes and Market Implications
Chapter 10 Global Cyber Risk Assessment Market Hotspots and Opportunities
- 10.1 Market Opportunity Mapping and Growth Hotspots
- 10.2 High-Growth Applications and Customer Groups
- 10.3 Underserved Markets and White-Space Opportunities
- 10.4 Emerging Technology and Product Opportunities
- 10.5 New Capacity and Investment Hotspots
- 10.6 Market Entry and Expansion Opportunities
- 10.7 Distribution and Partnership Opportunities
- 10.8 Near-Term and Long-Term Commercial Potential
- 10.9 Opportunity Attractiveness and Execution Risks
Chapter 11 Global Cyber Risk Assessment Market Outlook, 2024-2032
- 11.1 Market Size and Analysis
- 11.1.1 Revenue (Market Measurement: 2024: USD 245,622 million → 2032: USD 639,232 million)
- 11.1.2 Historical Market Size
- 11.1.3 Base-Year Market Size, 2024
- 11.2 Market Forecast, 2024-2032
- 11.2.1 Revenue Forecast to 2032
- 11.2.2 CAGR and Year-on-Year Growth
- 11.2.3 Incremental Revenue Opportunity
- 11.3 Forecast Assumptions and Scenario Analysis
- 11.3.1 Base-Case Forecast
- 11.3.2 Optimistic and Conservative Scenarios
- 11.3.3 Technology, Pricing and Policy Sensitivities
- 11.4 Market Attractiveness and Growth Outlook
Chapter 12 Global Cyber Risk Assessment Market Segmentation and Outlook
- 12.1 Segmentation Summary and Market Shares, 2024
- 12.2 Largest and Fastest-Growing Segments
- 12.3 By Service Type - Market Size and Forecast, 2024-2032
- 12.3.1 Segment Definition and Scope
- 12.3.2 Historical Market Size
- 12.3.3 Revenue Forecast, 2024-2032
- 12.3.4 Base-Year Market Share, 2024
- 12.3.5 Segment CAGR and Growth Drivers
- 12.3.6 Subsegment Market Size and Forecast
- 12.3.6.1 Consulting Services
- 12.3.6.2 Managed Services
- 12.3.6.3 Professional Services
- 12.3.7 Subsegment Pricing and Adoption Trends
- 12.3.8 Leading Suppliers and Competition
- 12.3.9 Regional Demand and Opportunities
- 12.4 By Solution Type - Market Size and Forecast, 2024-2032
- 12.4.1 Segment Definition and Scope
- 12.4.2 Historical Market Size
- 12.4.3 Revenue Forecast, 2024-2032
- 12.4.4 Base-Year Market Share, 2024
- 12.4.5 Segment CAGR and Growth Drivers
- 12.4.6 Subsegment Market Size and Forecast
- 12.4.6.1 Vulnerability Assessment
- 12.4.6.2 Risk Assessment
- 12.4.6.3 Threat Assessment
- 12.4.6.4 Penetration Testing Services
- 12.4.6.5 Security Program Assessment
- 12.4.7 Subsegment Pricing and Adoption Trends
- 12.4.8 Leading Suppliers and Competition
- 12.4.9 Regional Demand and Opportunities
- 12.5 By Deployment Mode - Market Size and Forecast, 2024-2032
- 12.5.1 Segment Definition and Scope
- 12.5.2 Historical Market Size
- 12.5.3 Revenue Forecast, 2024-2032
- 12.5.4 Base-Year Market Share, 2024
- 12.5.5 Segment CAGR and Growth Drivers
- 12.5.6 Subsegment Market Size and Forecast
- 12.5.6.1 On-Premises
- 12.5.6.2 Cloud-Based
- 12.5.7 Subsegment Pricing and Adoption Trends
- 12.5.8 Leading Suppliers and Competition
- 12.5.9 Regional Demand and Opportunities
- 12.6 By End-User Industry - Market Size and Forecast, 2024-2032
- 12.6.1 Segment Definition and Scope
- 12.6.2 Historical Market Size
- 12.6.3 Revenue Forecast, 2024-2032
- 12.6.4 Base-Year Market Share, 2024
- 12.6.5 Segment CAGR and Growth Drivers
- 12.6.6 Subsegment Market Size and Forecast
- 12.6.6.1 Banking, Financial Services, and Insurance (BFSI)
- 12.6.6.2 IT and Telecommunications
- 12.6.6.3 Government and Defense
- 12.6.6.4 Healthcare
- 12.6.6.5 Manufacturing
- 12.6.6.6 Retail
- 12.6.7 Subsegment Pricing and Adoption Trends
- 12.6.8 Leading Suppliers and Competition
- 12.6.9 Regional Demand and Opportunities
- 12.7 Segment Growth Comparison
- 12.8 Segment Attractiveness and Priority Matrix
Chapter 13 Global Cyber Risk Assessment End-Use and Application Market Outlook
- 13.1 End-Use Industry and Customer Demand Structure
- 13.2 Leading Applications and Customer Groups
- 13.3 End-Use Market Size, Share and Forecast
- 13.4 Major End-Use Industry Deep Dives
- 13.4.1 Customer Requirements and Use Cases
- 13.4.2 Demand and Replacement Cycles
- 13.4.3 Technical and Regulatory Considerations
- 13.4.4 Purchasing and Procurement Models
- 13.4.5 Leading Vendors and Distribution Channels
- 13.4.6 Forecast and Commercial Opportunities
- 13.5 Emerging Applications and Cross-Segment Demand
- 13.6 End-Use Industry Investment Priorities
Chapter 14 Global Cyber Risk Assessment Geographic Market Outlook, 2024-2032
- 14.1 Regional Market Size and Share, 2024
- 14.2 Regional Market Forecast, 2024-2032
- 14.3 Regional Pricing, Production and Demand Differences
- 14.4 North America
- 14.4.1 United States
- 14.4.2 Canada
- 14.4.3 Mexico
- 14.5 Europe
- 14.5.1 Germany
- 14.5.2 France
- 14.5.3 Italy
- 14.5.4 United Kingdom
- 14.5.5 Spain
- 14.5.6 Poland
- 14.5.7 Russia
- 14.5.8 Netherlands
- 14.5.9 Belgium
- 14.5.10 Sweden
- 14.5.11 Denmark
- 14.5.12 Norway
- 14.5.13 Rest of Europe
- 14.6 Asia Pacific
- 14.6.1 China
- 14.6.2 India
- 14.6.3 Japan
- 14.6.4 South Korea
- 14.6.5 Thailand
- 14.6.6 Indonesia
- 14.6.7 Vietnam
- 14.6.8 Malaysia
- 14.6.9 Australia
- 14.6.10 Rest of Asia Pacific
- 14.7 Latin America
- 14.7.1 Brazil
- 14.7.2 Argentina
- 14.7.3 Colombia
- 14.7.4 Chile
- 14.7.5 Rest of Latin America
- 14.8 Middle East
- 14.8.1 Saudi Arabia
- 14.8.2 United Arab Emirates
- 14.8.3 Turkey
- 14.8.4 Israel
- 14.8.5 Iran
- 14.8.6 Rest of the Middle East
- 14.9 Africa
- 14.9.1 South Africa
- 14.9.2 Egypt
- 14.9.3 Nigeria
- 14.9.4 Morocco
- 14.9.5 Rest of Africa
- 14.10 Regional Investment, Policy and Supply Chain Differences
- 14.11 Regional Competitive Landscape
- 14.12 Geographic Growth Hotspots
Chapter 15 Global Cyber Risk Assessment Technology, Innovation and Sustainability Outlook
- 15.1 Technology Landscape and Maturity
- 15.2 Product, Process and Service Innovation
- 15.3 AI, Automation and Digital Tools in the Industry
- 15.4 Technology Adoption and Performance Benchmarking
- 15.5 Innovation Pipeline and R&D Investment
- 15.6 Patent and Intellectual Property Trends
- 15.7 Energy Efficiency and Resource Management
- 15.8 Sustainability, Recycling and Circularity
- 15.9 Technology Roadmap, 2024-2032
- 15.10 Risks of Obsolescence and Technology Substitution
Chapter 16 Global Cyber Risk Assessment Market Key Strategic Imperatives
- 16.1 Growth and Market Entry Priorities
- 16.2 High-Return Products and Segments
- 16.3 Pricing, Profitability and Cost Optimization
- 16.4 Technology Investment and Product Differentiation
- 16.5 Supply Chain Localization and Resilience
- 16.6 Distribution and Customer Acquisition
- 16.7 Partnership, Acquisition and Capacity Strategy
- 16.8 Regional Expansion Priorities
- 16.9 Short-, Medium- and Long-Term Actions
Chapter 17 Competition Outlook
- 17.1 Industry Competition Characteristics
- 17.2 Market Structure and Concentration
- 17.3 Market Share and Competitive Positioning, 2024
- 17.4 Company-Wise Revenue and Product Benchmarking
- 17.5 Production and Service Capacity Benchmarking
- 17.6 Technology, Pricing and Differentiation
- 17.7 Regional Footprint and Distribution Strength
- 17.8 Mergers, Acquisitions and Strategic Alliances
- 17.9 New Entrants and Competitive Threats
- 17.10 Porter's Five Forces and Industry Attractiveness
- 17.11 Competitive Outlook, 2024-2032
Chapter 18 Company Profiles
- 18.1 Company Coverage and Selection Criteria
- 18.2 IBM
- 18.2.1 Business Description
- 18.2.2 Company Ownership and Geographic Presence
- 18.2.3 Product and Service Portfolio
- 18.2.4 Manufacturing and Operating Footprint
- 18.2.5 Financial Performance and Investment
- 18.2.6 Market Share and Competitive Position
- 18.2.7 Technology and Innovation Capabilities
- 18.2.8 Strategic Alliances or Partnerships
- 18.2.9 Recent Developments
- 18.2.10 Growth Strategy and Outlook
- 18.3 Palo Alto Networks
- 18.4 Rapid7
- 18.5 CrowdStrike
- 18.6 Cisco
- 18.7 Sophos
- 18.8 Zscaler
- 18.9 Astra Security
- 18.10 Qualysec
- 18.11 Secureworks
- 18.12 Other Relevant Market Participants
Note: Every listed company is profiled on the structure shown under the first company. The company list is preliminary and may change based on research findings, market developments, data availability and client requirements.
Chapter 19 Disclaimer
- 19.1 Research and Forecast Disclaimer
- 19.2 Data Source and Estimation Limitations
Note: The depth of individual sections depends on data availability for this market. Volume, capacity, trade and other unit-based metrics are included where applicable.

